
Saudi Military Hospital Hack Claim Includes Patient and Staff Samples
Overview
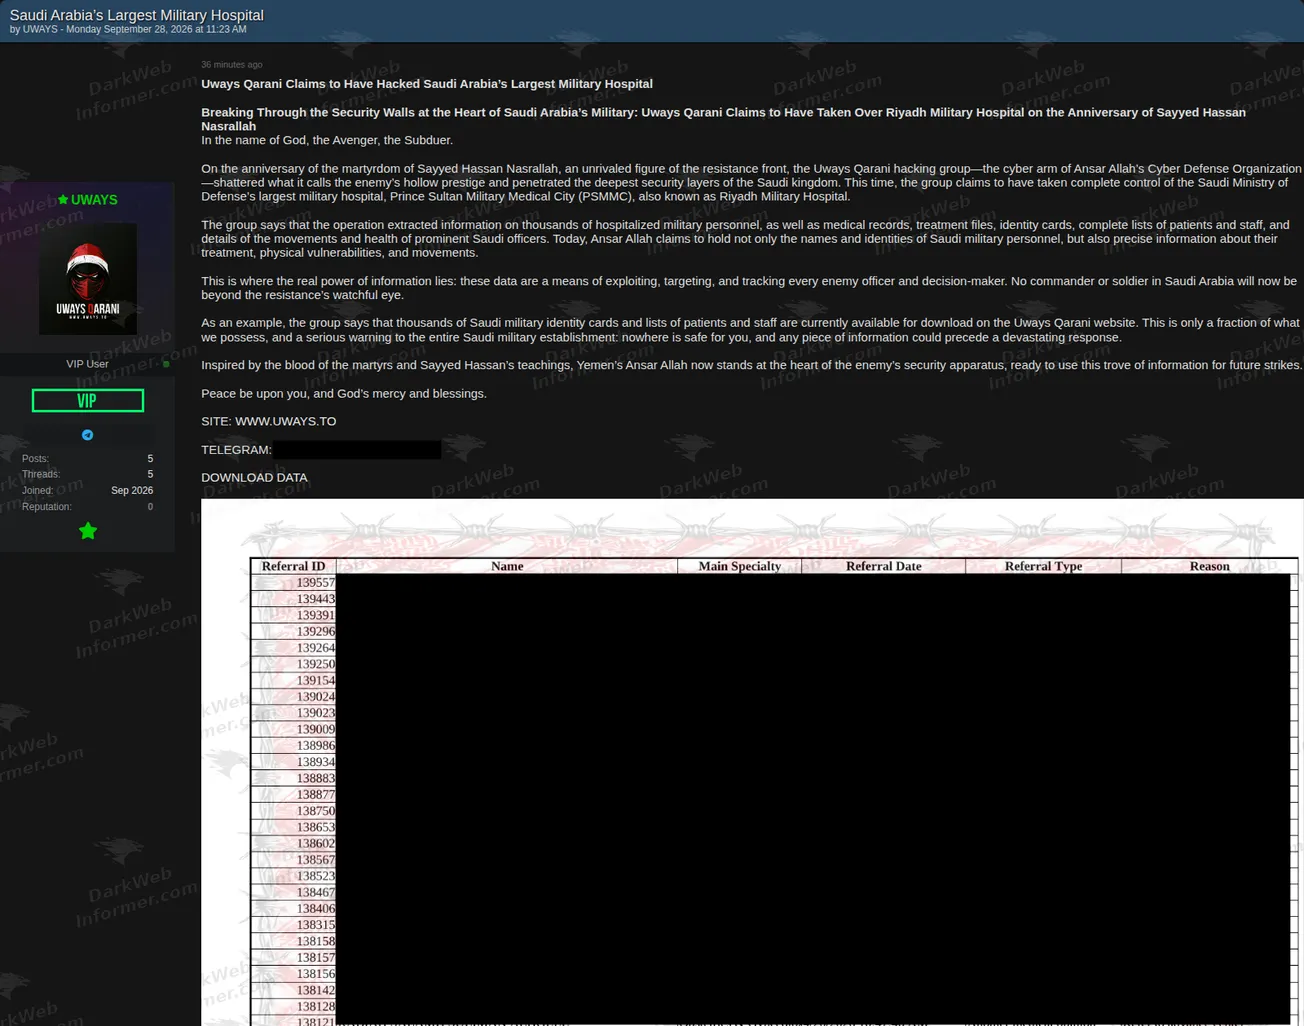
A poster using the handle "UWAYS", writing on behalf of Uways Qarani, claims to have penetrated systems associated with Prince Sultan Military Medical City (PSMMC), also referred to in the post as Riyadh Military Hospital. The group claims it obtained information on thousands of Saudi military personnel, as well as patient and staff records, treatment details and identity documents.
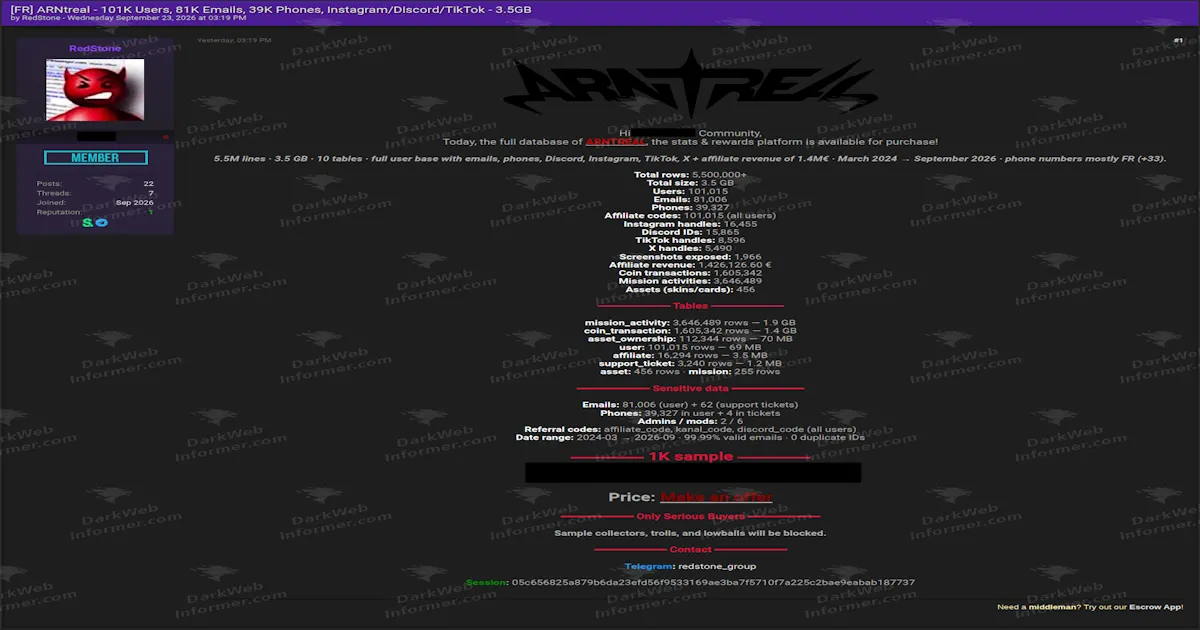
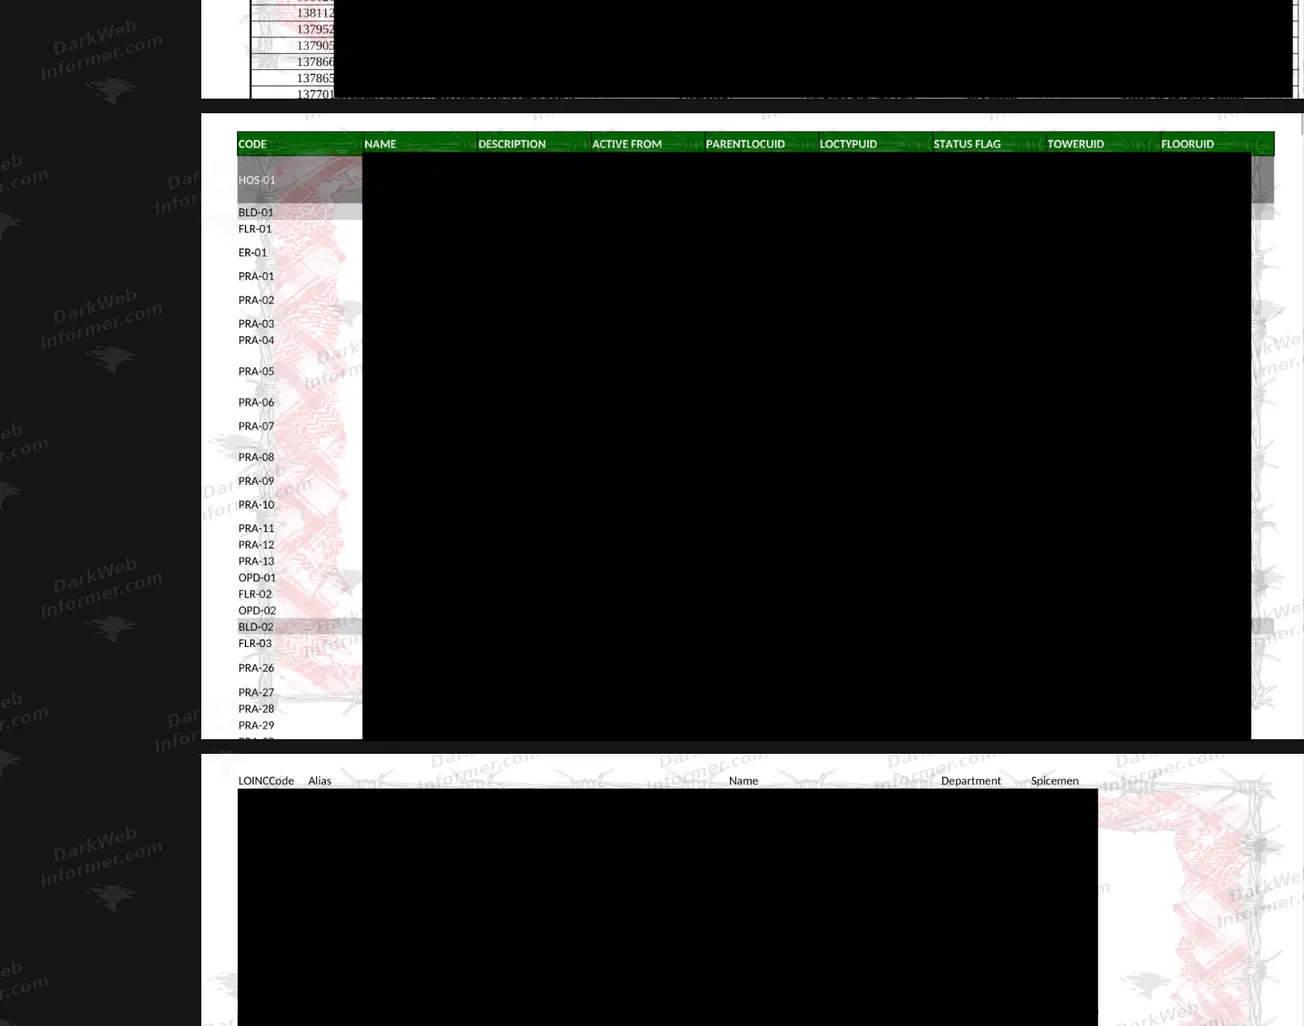
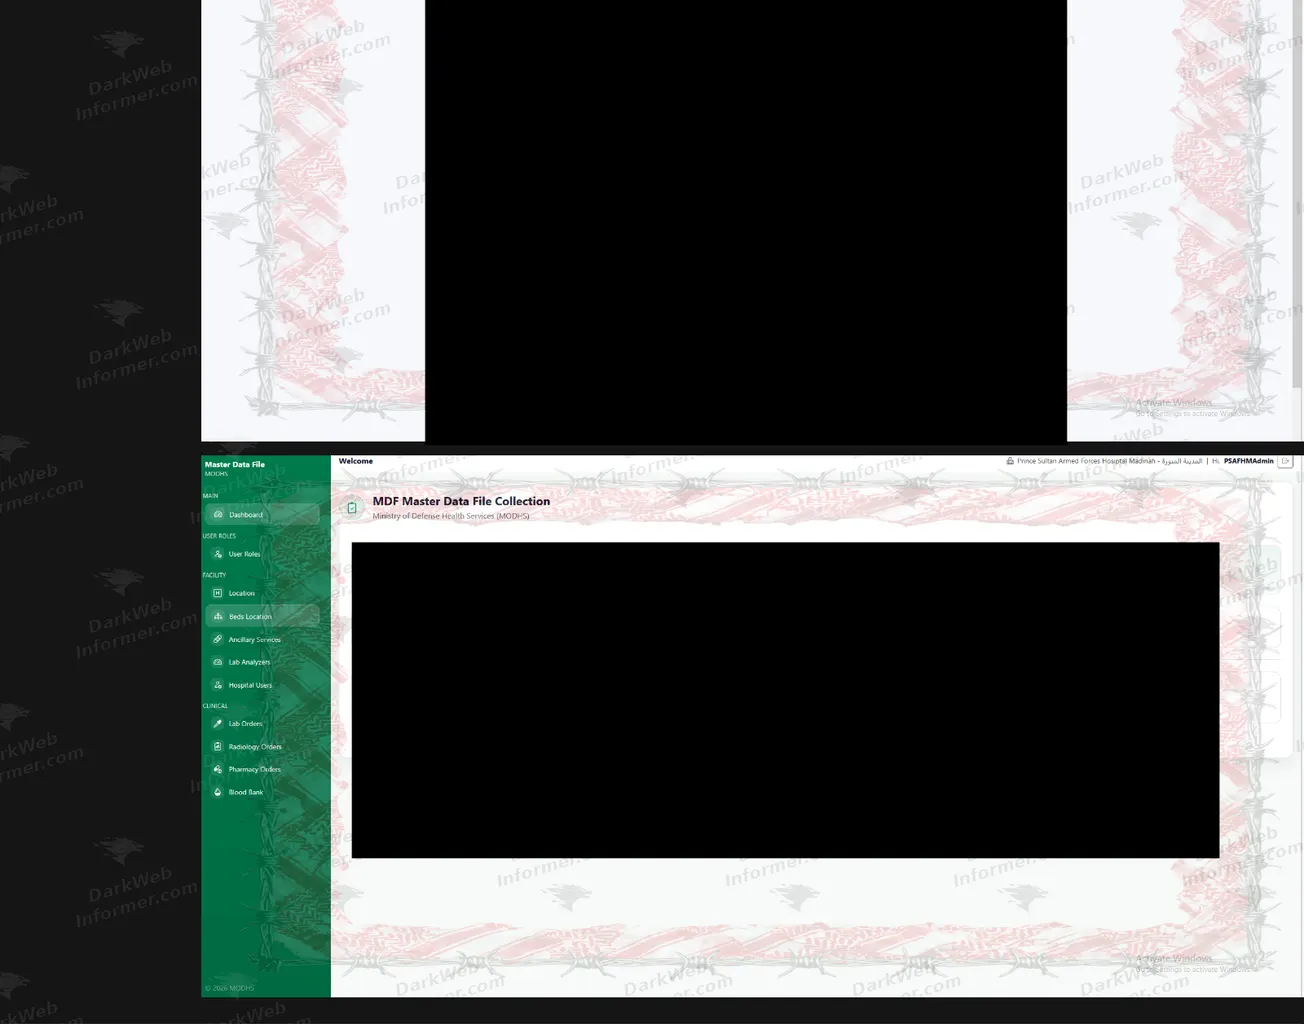
Six supplied captures show the statement and purported samples: a patient referral table, hospital location and laboratory lists, a staff roster, identity card thumbnails, and hospital administration screens. One sample dashboard names Prince Sultan Armed Forces Hospital Madinah, a different facility label from the Riyadh institution in the claim. The intrusion, origin, completeness and scale of the data have not been independently verified.
Post details
What the post claims
- Complete control of the named military hospital claimed
- Information on thousands of military personnel claimed extracted
- Medical records and treatment files claimed
- Patient and staff lists claimed available
- Military identity cards claimed available
- Patient referral table shown
- Staff roster with roles and contact fields shown
- Hospital location and department metadata shown
- Laboratory test catalog shown
- Identity document thumbnails shown
- Hospital admin dashboard screenshots shown
- Data advertised for download on the group site
The post claims access to a Riyadh military hospital. A sample dashboard instead names a Madinah facility. The screenshots do not establish that either institution was compromised or that the claimed download contains all the categories described.
Screenshots
IOCs & contact identifiers
Identifiers visible in the listing. These support correlation and do not independently establish access to the named institutions.
| Type | Identifier | Source |
|---|---|---|
| Poster | UWAYS | Screenshot 1 |
| Group website | uways[.]to | Screenshot 1 |
| Telegram contact | @UWAYS_QARANI | Screenshot 1 |
The website and Telegram handle are advertised contact points in the post; the screenshots do not establish who controls them. No Tox ID, Session ID, malware hash or attacker-controlled IP address is visible. Patient, staff and identity-document identifiers shown in the purported samples are not included in this table. URLs to any data will always be blurred out, but are available to subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Inferred The group claims to have extracted hospital personnel and medical records. The tabular and administrative samples are consistent with stored records, but do not show how they were obtained.
Potential impact
If authentic, disclosure of patient referrals, medical details, staff rosters and identity cards could expose sensitive health and identity information. The claim also references military personnel and movements, which could create further risks if supported by the underlying material. The visible dashboard's 1,105 users is a count displayed in that interface, not a verified breach or victim count.
Status Unverified
Dark Web Informer has not independently verified the claimed intrusion, control of hospital systems, number of affected people, or authenticity and source of the records. The visible samples contain a Madinah facility label while the post names PSMMC in Riyadh, and that relationship is unresolved. Screenshots of records and application interfaces do not demonstrate the attack path or current control of a live system. No independent response from the named hospital or Saudi authorities is present in the supplied material.