Alleged Pet Stop Dataset With 1M+ Records Offered for $140
Overview
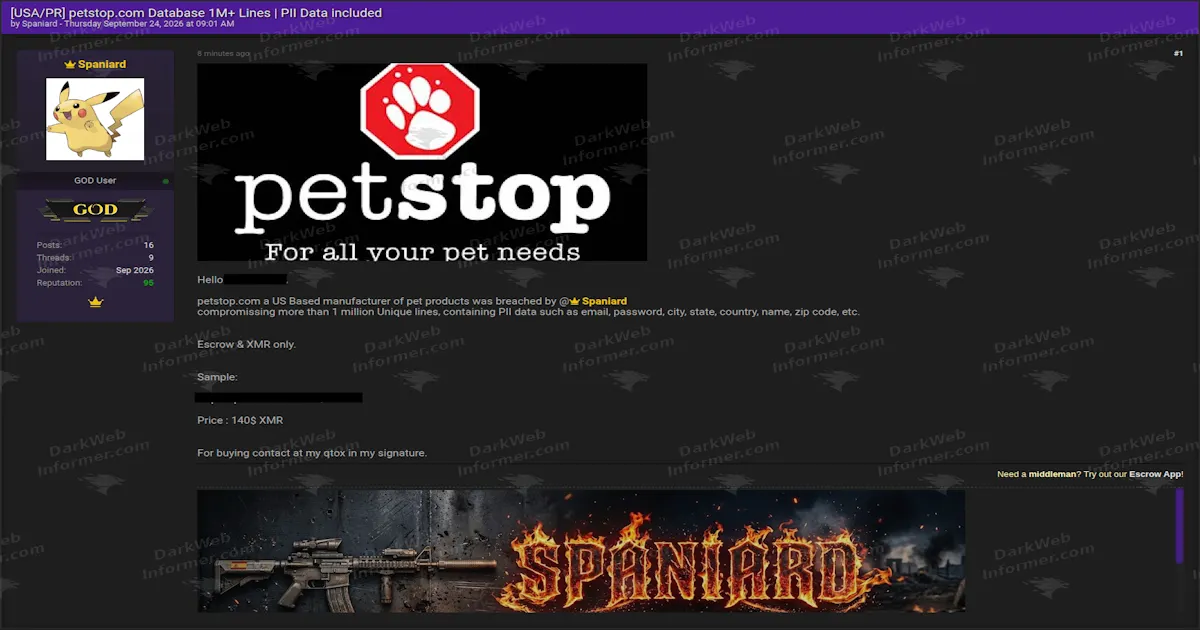
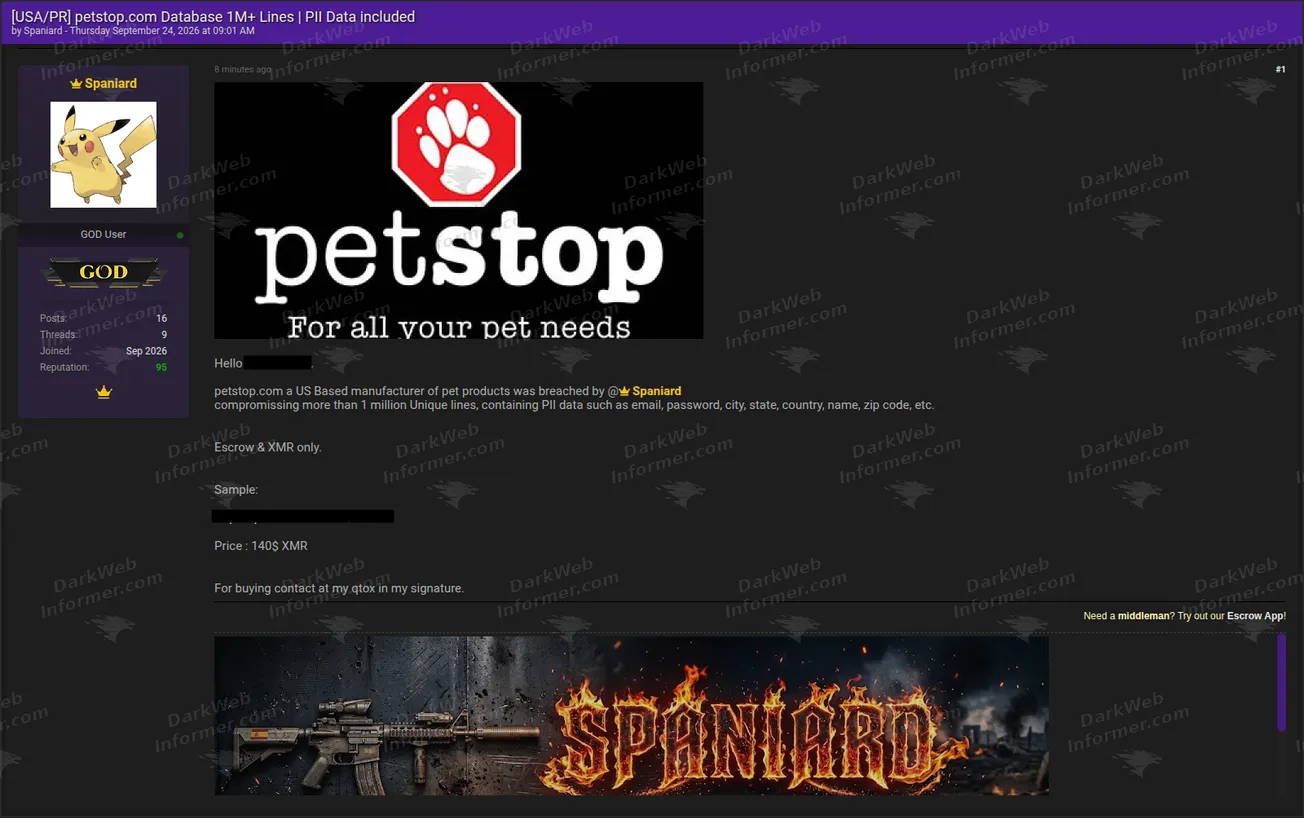
An actor using the handle "Spaniard" claims to have breached Pet Stop and is offering an alleged dataset containing more than one million unique lines for $140, payable in Monero (XMR). The post identifies the target as petstop.com and describes it as a US-based manufacturer of pet products.
The actor claims the dataset includes email addresses, passwords, names, cities, states, countries and ZIP codes. The listing specifies escrow and XMR-only payment and refers buyers to a qTox contact in the actor's signature. A sample-data URL is shown in the source and blurred in this report's screenshot. The alleged breach, dataset authenticity, record count and password format have not been independently verified.
Post details
What the post claims
- Breach of Pet Stop claimed
- More than 1 million unique lines claimed
- Email addresses
- Passwords, with storage format unspecified
- Names
- Cities and states
- Countries and ZIP codes
- $140 asking price, payable in Monero
- Escrow and XMR-only payment terms
Screenshots
IOCs & contact identifiers
Identifiers visible in the source material. The actor handle supports correlation and does not, on its own, establish compromise.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Spaniard | Screenshot 1 |
| Named organization domain | petstop[.]com | Screenshot 1 |
The domain identifies the organization named in the claim, not malicious infrastructure. The post mentions qTox, but no Tox ID is visible in the supplied screenshot. No Telegram handle, Session ID, malware hash or attacker-controlled IP address is visible. The sample-data URL is omitted from this table. URLs to any data will always be blurred out, but are available to subscribers on the threat feed or ransomware feed.
Mapped techniques
No MITRE ATT&CK technique is assigned from this screenshot alone. The actor claims a breach and offers data for sale but does not establish an initial-access vector, collection method or exfiltration mechanism. The reference to passwords does not show credential dumping, password cracking or the format in which those passwords are stored.
Potential impact
If authentic, the claimed combination of names, email addresses and location fields could support targeted phishing, impersonation and profiling. Exposure of usable passwords could create account-takeover risk, including on other services where the same credentials are reused. The listing does not establish whether the alleged passwords are plaintext, hashed or otherwise protected. More than one million lines does not establish one million distinct affected people.
Status Unverified
Dark Web Informer has not independently verified the alleged breach, the actor's access, dataset ownership, record count or data accuracy. The screenshot contains an advertisement and a sample link, but no sample records are displayed. The linked sample was not accessed for this report. The source does not establish the age of the records, whether the dataset is new or recycled, or whether it contains duplicate identities. No company confirmation or technical evidence of the intrusion is included.