 South Africa
Healthcare
Patient & Internal Data
Leak Claim
Unverified
Ampath Laboratories Data Breach Claim Says 10 Databases Copied, Including 80M+ Admission Records
Overview
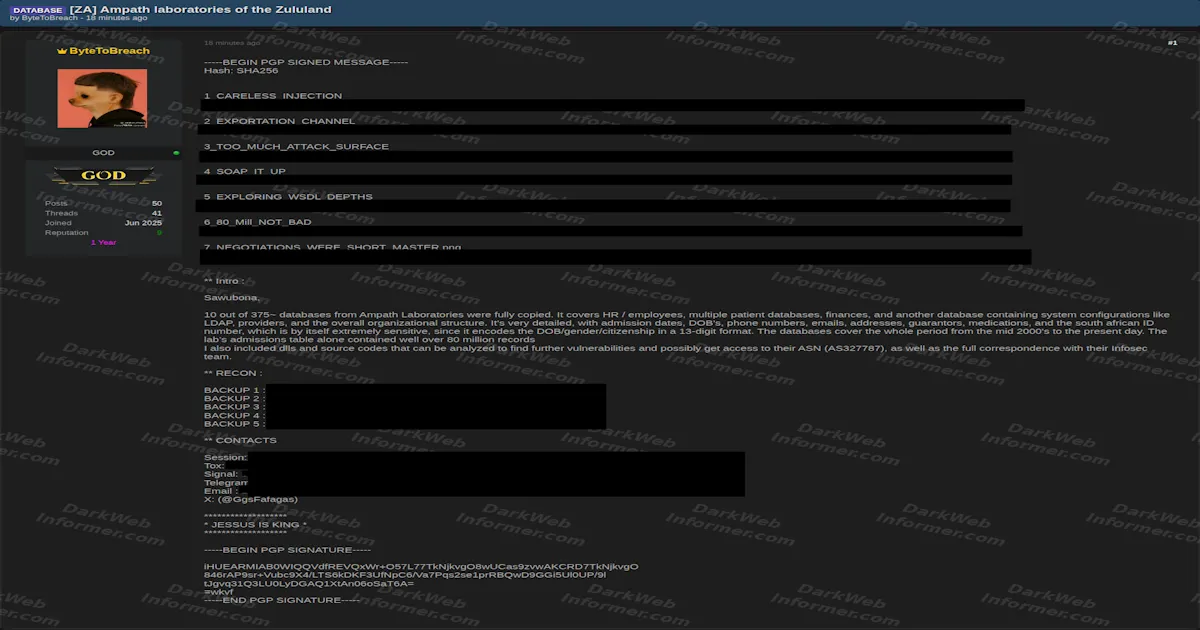
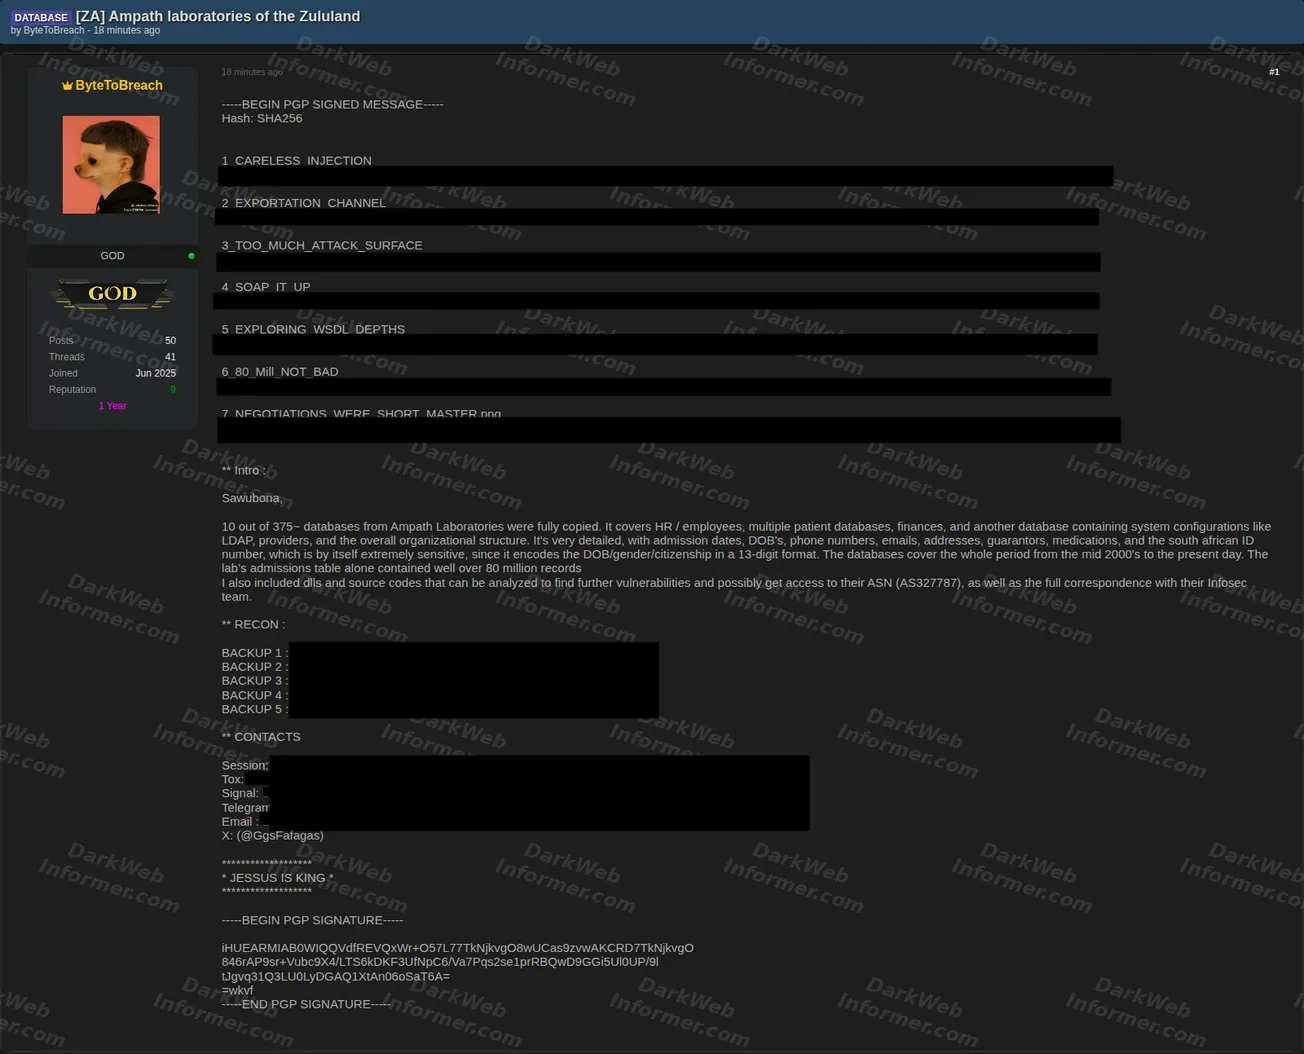
An actor using the handle "ByteToBreach" claims to have copied 10 databases from Ampath Laboratories out of an environment containing roughly 375 databases. The post says the material includes HR and employee data, multiple patient databases, financial information and system-configuration data.
The actor claims the datasets contain admission dates, dates of birth, phone numbers, email addresses, physical addresses, guarantor information, medications and South African ID numbers. The post further states that the laboratory admissions table alone contains more than 80 million records and that the databases cover a period from the mid-2000s through the present. Source code, DLLs and correspondence with the organization's information-security team are also claimed to be included. The authenticity, source, completeness and stated record volumes have not been independently verified.
Post details
South AfricaWhat the post claims
- 10 databases fully copied
- Roughly 375 databases referenced in the environment
- HR and employee data included
- Multiple patient databases included
- Financial data included
- System-configuration data included
- LDAP and provider information referenced
- Admission dates included
- Dates of birth included
- Phone numbers and email addresses included
- Physical addresses included
- Guarantor information included
- Medication information included
- South African ID numbers included
- 80M+ records claimed in the admissions table alone
- Data spanning the mid-2000s to present
- DLLs and source code included
- Infosec-team correspondence included
The actor also references AS327787 and claims the included code and libraries could be analyzed for additional vulnerabilities. Multiple backup and download locations are shown in the source material; those links are not reproduced in this report.
Screenshots
IOCs & contact identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the breach claim or identify the individual behind the account.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | ByteToBreach | Screenshot 1 |
| Session ID | 05c2db4775cb46350f16814dfe3bfa856664f315585653e4c368af08ce50b0c31b | Screenshot 1 |
| Tox ID | 947E4A3A16ECF3A15E2F7183BC4CA6B2CD28F1E96F25A2694F4CA145FCBD457266414CD68287 | Screenshot 1 |
| Signal | bytetobreach.83 | Screenshot 1 |
| Telegram | @Bytetobreach33 | Screenshot 1 |
Bytetobreach@tuta.com | Screenshot 1 | |
Dookhl0yka@outlook.com | Screenshot 1 | |
bytetobreach33@pm.me | Screenshot 1 | |
| X handle | @GgsFafagas | Screenshot 1 |
| Referenced ASN | AS327787 | Screenshot 1 |
No malware hash or attacker-controlled IP address is visible in the supplied material. The source screenshot contains multiple direct backup and download links to the purported data; those links are intentionally not reproduced here. Patient, employee and other personal identifiers referenced in the claim are not included in this table.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Claimed The actor explicitly claims to have copied multiple databases containing patient, employee, finance and system-configuration information.
Potential impact
If authentic, the claimed exposure could be highly sensitive because it combines patient information, medication data, South African ID numbers, employee records, financial information and internal system configuration. That combination could increase risks of identity fraud, targeted phishing, extortion, privacy violations and further compromise of internal infrastructure.
Status Unverified
Dark Web Informer has not independently verified the authenticity, source, completeness, database counts, 80M+ admission-record claim, code repositories or current availability of the purported material. The supplied screenshot documents the actor's claims and contact information, not independent confirmation of the underlying data.