Digit RE Group Call and Contact Data Allegedly Leaked
Overview
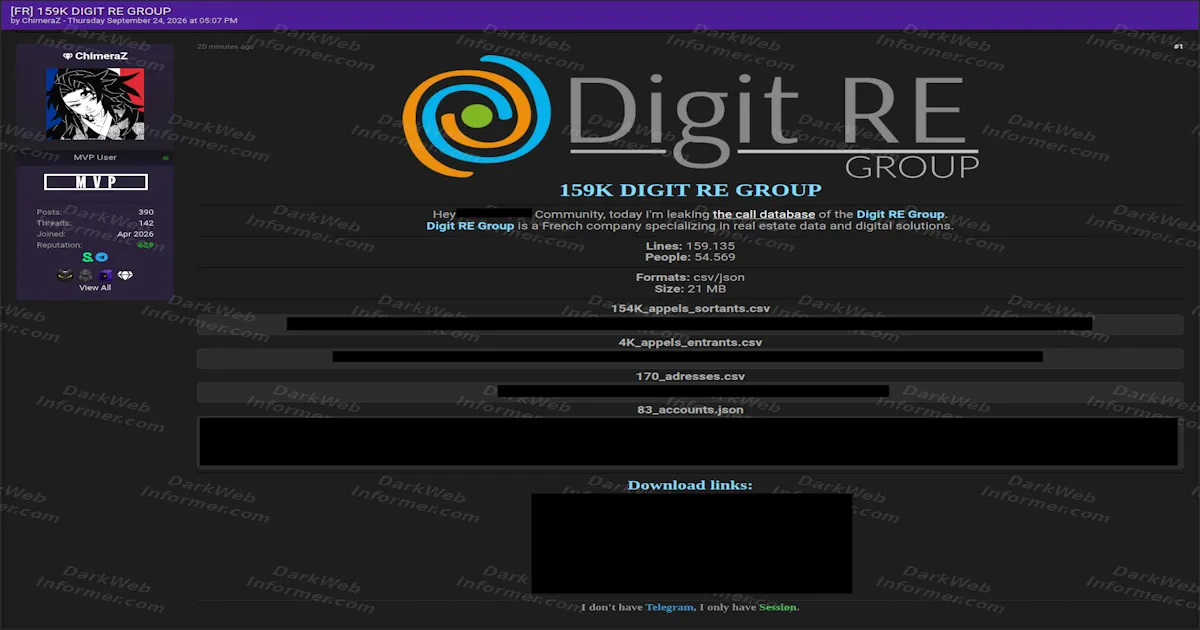
An actor using the handle "ChimeraZ" claims to have released call-related data associated with Digit RE Group. The listing describes the organization as a French company specializing in real estate data and digital solutions, and advertises 159,135 lines involving 54,569 people in a 21 MB dataset supplied in CSV and JSON formats.
The screenshot shows samples labeled as outbound calls, inbound calls, contacts and telephony accounts. Visible fields include timestamps, telephone numbers, names, email addresses, extensions and account configuration details. The account sample also contains a Linphone provisioning URL with a key parameter, whose validity and privileges are unknown. The dataset's authenticity, origin, counts and connection to a compromise of Digit RE Group have not been independently verified.
Post details
What the post claims
- 159,135 total lines claimed
- 54,569 people claimed
- 21 MB dataset in CSV and JSON
- 154K_appels_sortants.csv: outbound calls
- 4K_appels_entrants.csv: inbound calls
- 170_adresses.csv: contact/address-book entries
- 83_accounts.json: telephony account entries
- Call timestamps and telephone numbers
- Caller or account names and internal identifiers
- Call status, service and plan-related fields
- Names, phone numbers and email addresses in contacts
- Local extensions and assigned telephone numbers
- Telephony server and account-management references
- Linphone provisioning URL with a key parameter
- Sample call timestamps from August 6-7, 2026
- Session mentioned; no Session ID visible
The numbers in the filenames are source labels, not independently counted file contents. The post does not explain how it calculated the claimed people count or removed duplicates. The visible examples contain call metadata; no call audio or transcripts are shown.
Screenshots
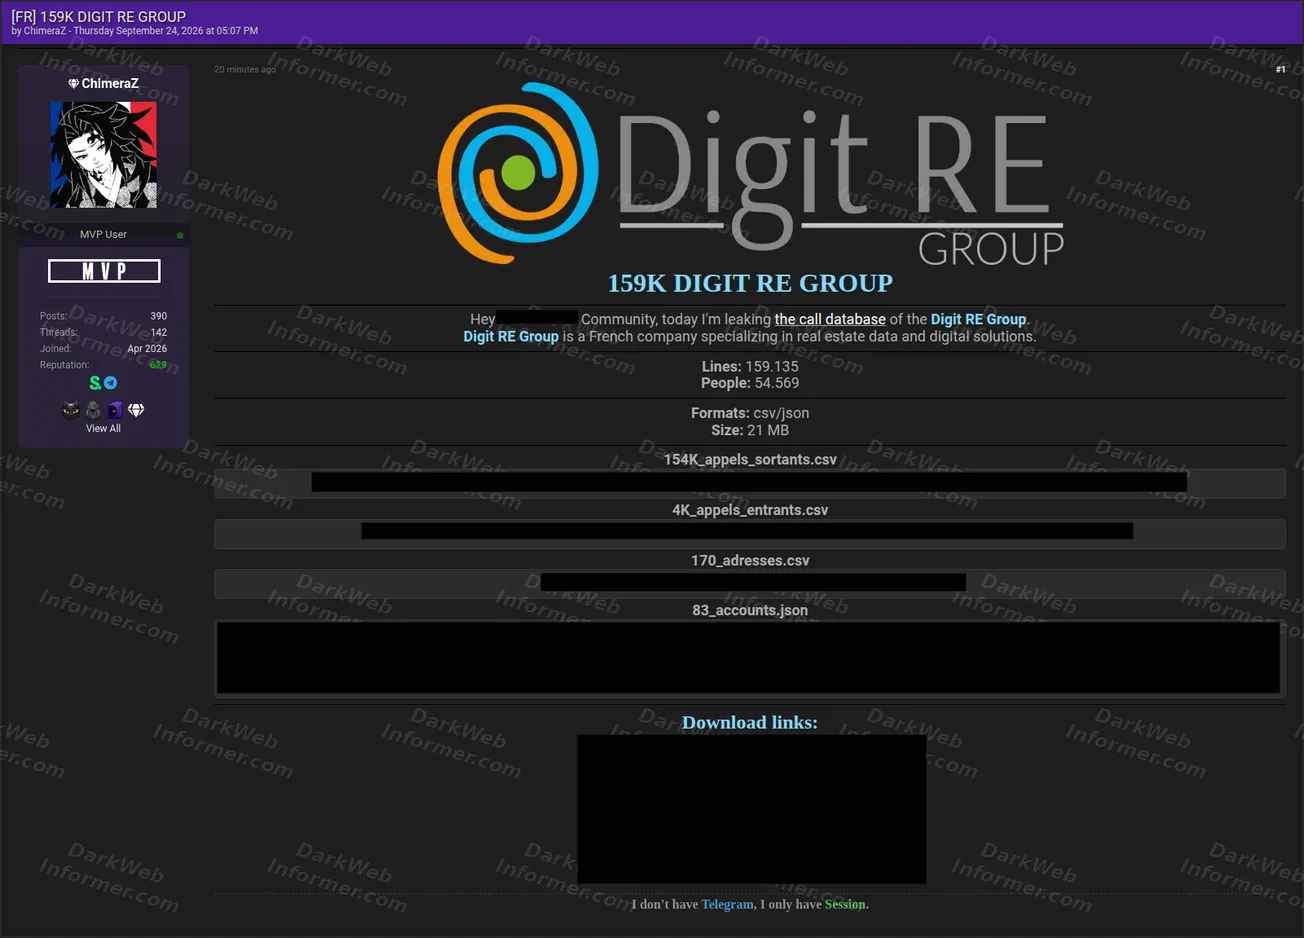
IOCs & contact identifiers
Identifiers and contextual infrastructure references visible in Screenshot 1. The service hosts are included for correlation, not as confirmed malicious infrastructure.
| Type | Identifier | Source in Screenshot 1 |
|---|---|---|
| Actor handle | ChimeraZ | Author and profile |
| Organization domain in sample | digitregroup[.]com | Contact email domain |
| Telephony server in sample | cx14c[.]axialys[.]net | Account server field |
| Provisioning host in sample | voiprov[.]axialys[.]net | Provisioning URL host |
| Account-management host in sample | centrex[.]service-centrex[.]com | Account and offer references |
The organization domain identifies the entity named in the claim, not malicious infrastructure. The other hosts occur in the purported telephony configuration; their presence does not establish that the service providers were compromised. The actor says they use Session, but no Session ID is visible. No Tox ID, Telegram handle, malware hash or attacker-controlled IP address is visible. Customer identifiers, account-specific paths, the provisioning key and data-download URLs are excluded from this table. URLs to any data will always be blurred out, but are available to subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Claimed The actor claims to release a call dataset and presents exported call, contact and account records. This maps the claimed collection of database contents; the access vector, database engine and export method are not established.
- Credential Access T1552.001 Unsecured Credentials: Credentials In Files Inferred The JSON account sample contains a provisioning URL with a key parameter. This supports an inferred mapping to potentially exposed credential material in a file. The key's authentication role, validity and usability are unverified; no use of it is demonstrated.
Potential impact
If authentic, names, telephone numbers, email addresses and call histories could support targeted phishing, voice scams, impersonation and analysis of business relationships. Account and service configuration fields could reveal details of the telephony environment. A usable provisioning key could create additional access risk, depending on its permissions and current validity. The screenshot does not demonstrate successful account access, intercepted calls or exposure of call recordings.
Status Unverified
Dark Web Informer has not independently verified the dataset's authenticity, origin, completeness, line count or claimed people count. The supplied screenshot shows brief examples rather than the full files. Call timestamps from August 2026 and an account registration field from June 2026 do not establish the breach date or the full period covered. The data-download links and service endpoints were not accessed, and the provisioning key was not tested. The source does not establish whether the data came directly from Digit RE Group, a service provider, an export or another source. No company confirmation or independent technical evidence of an intrusion is included.