
Actor Offers KEL Group Data for Sale, Claims 1.3 Million People Affected
Overview
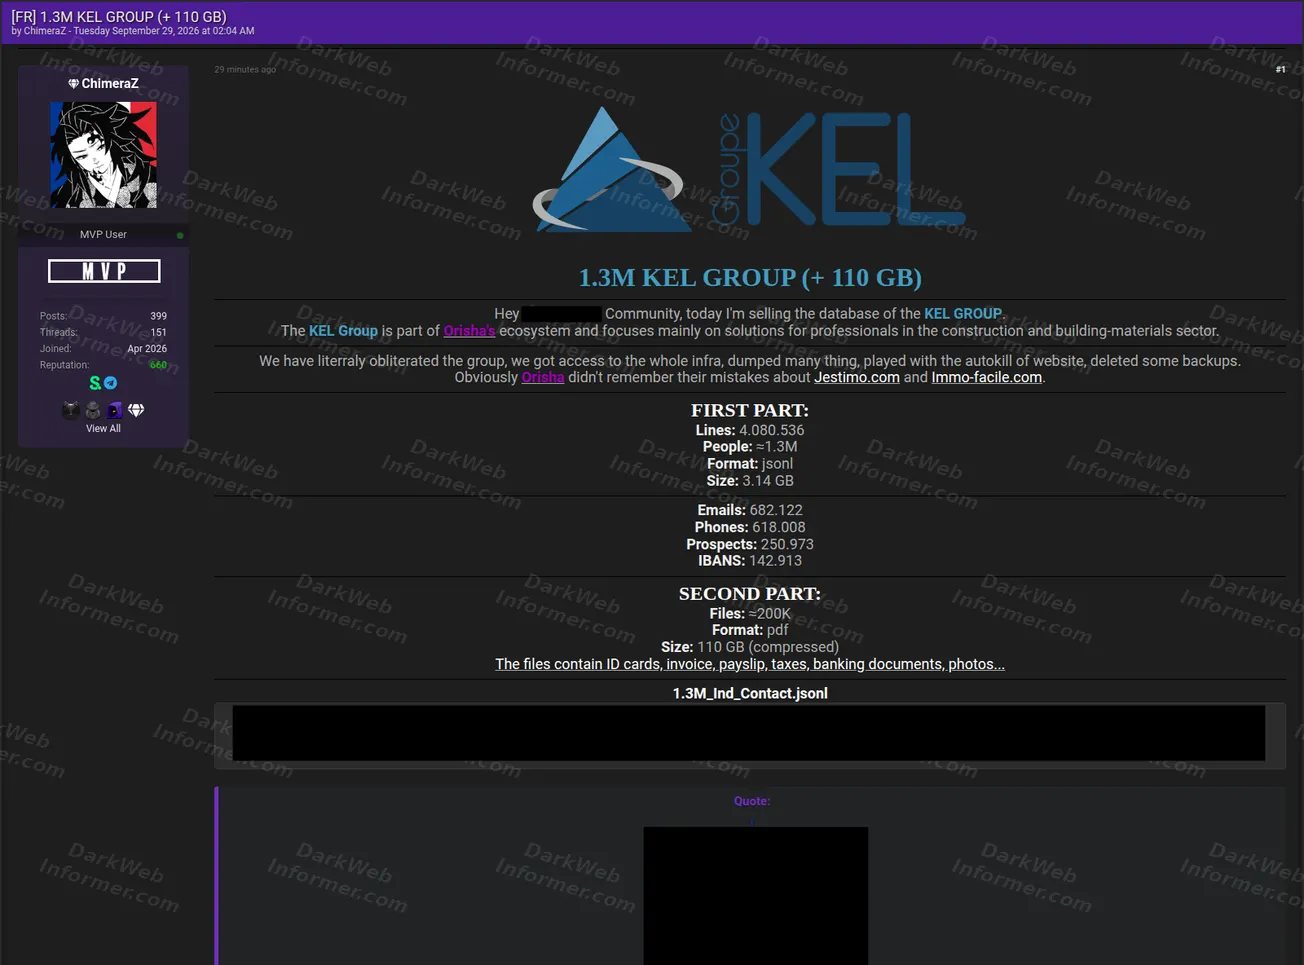
An actor using the handle "ChimeraZ" is offering what they describe as the KEL Group database for sale. The post identifies KEL Group as part of Orisha’s ecosystem serving construction and building-materials professionals. It claims access to the organization’s infrastructure, a full data dump, a website disruption and deletion of some backups.
The actor splits the offer into 4,080,536 lines relating to approximately 1.3 million people in a 3.14 GB JSONL first part and approximately 200,000 PDF files totaling 110 GB compressed in a second part. The post lists email addresses, phone numbers, prospects and IBANs, along with identity documents, invoices, payslips, tax and banking records. Visible structured samples contain personal and credential-related fields. The claimed access, volume and contents have not been independently verified.
Post details
What the post claims
- Whole infrastructure access and data dump claimed
- Website disruption and some backup deletion claimed
- 4,080,536 lines in the first part
- Approximately 1.3 million people claimed
- 3.14 GB first part in JSONL format
- 682,122 emails and 618,008 phone numbers listed
- 250,973 prospects and 142,913 IBANs listed
- Approximately 200,000 PDF files in the second part
- 110 GB compressed size claimed for PDFs
- Identity, payroll, tax and banking documents listed
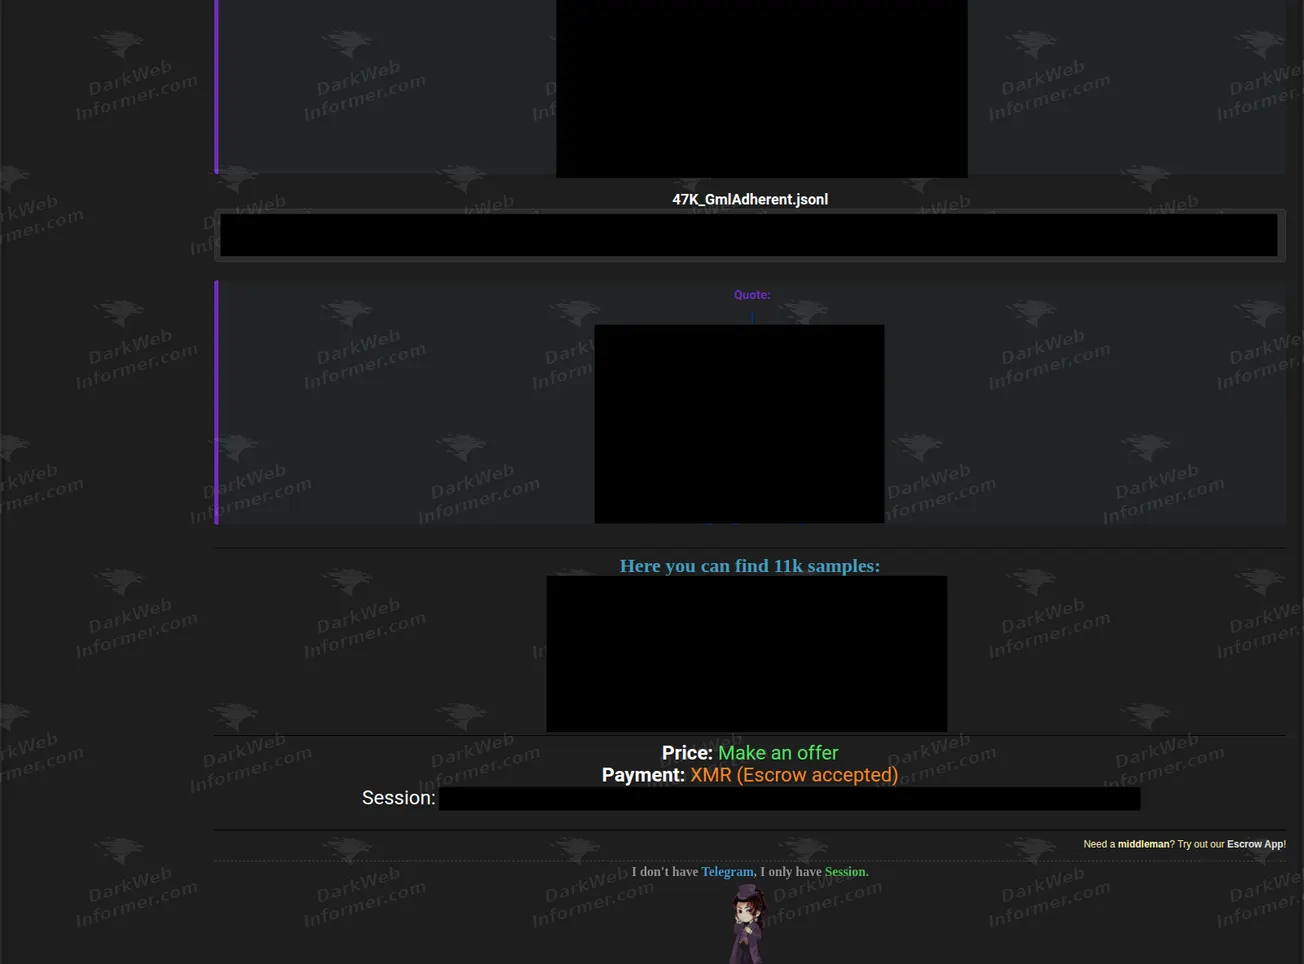
- Approximately 11,000 samples advertised via data links
- Price by offer; XMR payment and escrow accepted
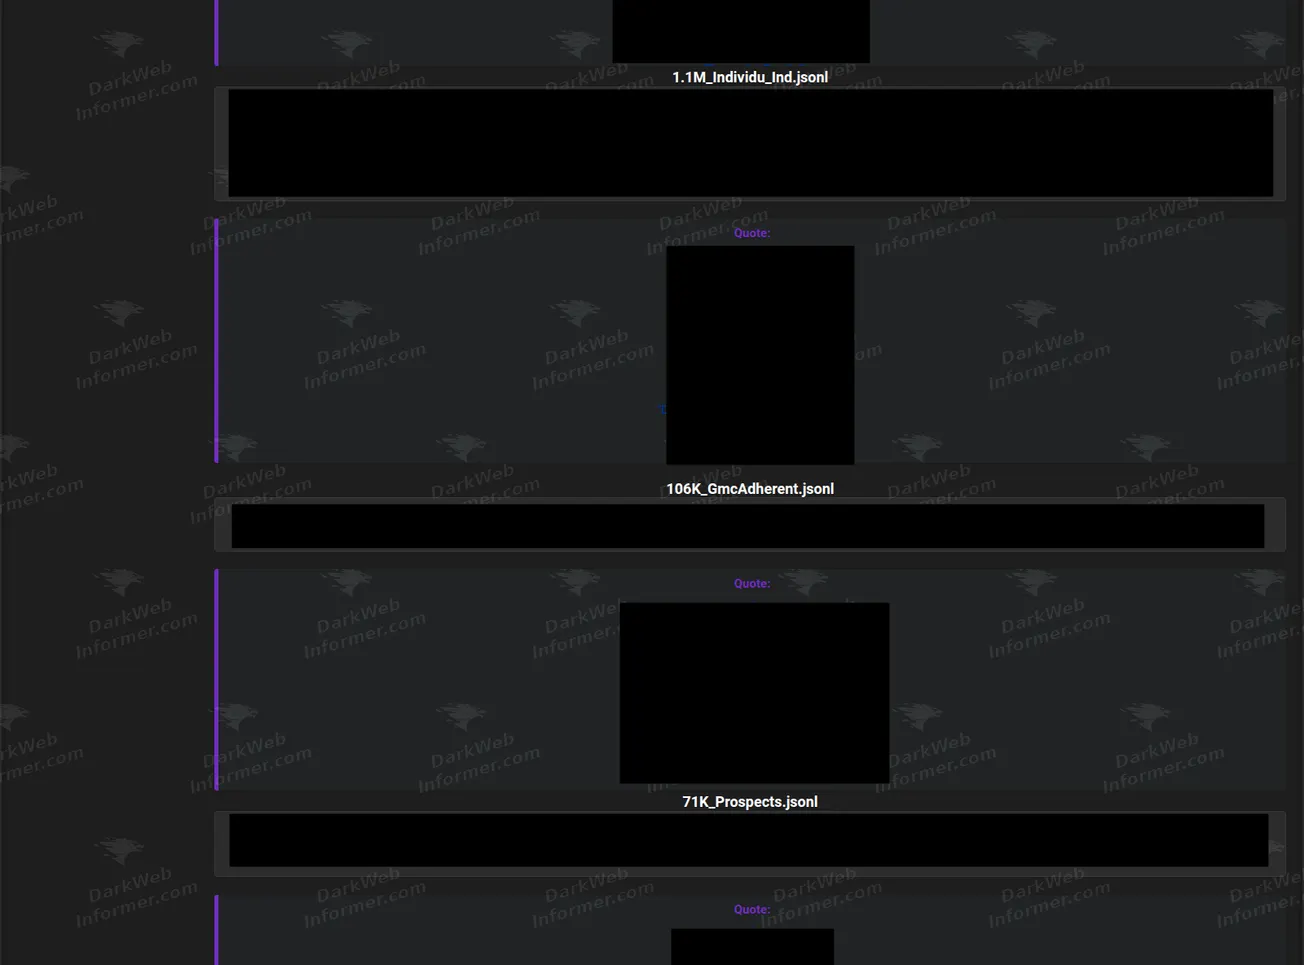
The visible JSONL snippets show contact, address, account and credential-related field names. They do not prove the advertised totals or confirm that all records belong to distinct people. The second part’s PDF count and size are claims in the listing; the supplied captures do not display the complete archive.
Screenshots
IOCs & contact identifiers
Identifiers visible in the listing. These support correlation and do not independently establish unauthorized access.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | ChimeraZ | Screenshot 1 |
| Session ID | 05c1396ee8a9d6df7ae4497a07f2fbc75b31344f5e0cbd91dacde4c04c88c4c254 | Screenshot 3 |
No Tox ID, Telegram handle, malware hash or attacker-controlled IP address is visible. The organization names and comparison domains in the post are contextual references, not identified malicious infrastructure. Customer identifiers in the purported samples are not included in this table. URLs to any data will always be blurred out, but are available to subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Inferred The actor describes a database dump and displays structured JSONL records. The access path and collection method are not shown.
- Impact T1490 Inhibit System Recovery Claimed The actor says they deleted some backups. The claim is unsupported by technical evidence in the supplied captures.
Potential impact
If authentic, the claimed data could expose contact information, financial identifiers and sensitive documents for customers and other individuals. The sample also shows credential-related fields. The claimed website disruption and backup deletion could affect service availability and recovery. The post alone cannot establish the number of affected people or the extent of any operational impact.
Status Unverified
Dark Web Informer has not independently verified the actor’s access to KEL Group or Orisha systems, the full dataset, the stated record and file counts, the website disruption or the backup deletion. The supplied captures show excerpts rather than the full files, and do not include a response from the named organization.