
Horizane Santé Breach Claim Includes 8,864 Customer Records
Overview
An actor using the handle "Jaded" claims to have breached Horizane Santé and exposed records relating to 8,864 active customers, alongside 12 employee records. The post describes the organization as a French health, wellness and parapharmacy company. Its title also claims admin access.
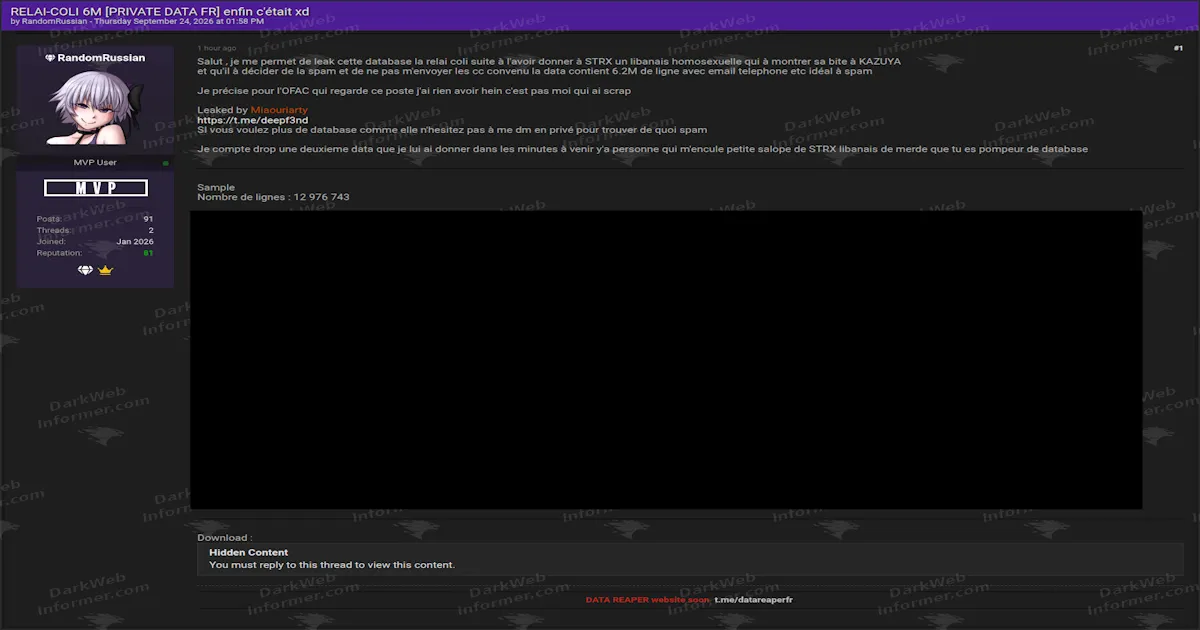
The actor claims the customer data includes bcrypt password hashes. A visible sample shows customer names, email addresses, account identifiers, active-status fields, creation timestamps and default-group identifiers. The screenshot also lists employee-data field names and a download area hidden behind a forum points unlock. The breach, record counts, password-hash exposure and admin access have not been independently verified.
Post details
What the post claims
- Breach of Horizane Santé claimed
- 8,864 active customer records claimed
- 12 employee records claimed
- bcrypt password hashes claimed for customer accounts
- Admin access claimed in the post title
- Customer sample includes names and email addresses
- Customer sample includes IDs, active status and creation dates
- Customer sample includes default-group identifiers
- Employee fields include profile IDs and last_passwd_gen
Screenshots

IOCs & contact identifiers
Identifier visible in the source material. The actor handle supports correlation and does not, on its own, establish compromise.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Jaded | Screenshot 1 |
No Telegram handle, Tox ID, Session ID, malware hash or attacker-controlled IP address is visible. Customer names and email addresses shown in the purported evidence are not included in this table. The download destination is hidden in the supplied screenshot. URLs to any data will always be blurred out, but are available to subscribers on the threat feed or ransomware feed.
Mapped techniques
No MITRE ATT&CK technique is assigned from this screenshot alone. The post claims a breach and admin access but does not show how access was obtained, how data was collected or how it was exfiltrated. The claim of bcrypt password-hash exposure does not establish a password-cracking attempt, and the admin access claim does not identify an authentication method.
Potential impact
If authentic, exposure of customer names, email addresses and account metadata could support targeted phishing, impersonation and other account-focused abuse. Claimed password-hash exposure could create additional account risk if passwords are recovered and reused elsewhere. Employee-data exposure and genuine admin access could broaden the potential impact, but the screenshot does not demonstrate administrative control or its scope. It does not establish exposure of payment-card details, medical records or health information.
Status Unverified
Dark Web Informer has not independently verified the alleged breach, the actor's access, the record counts or the origin and completeness of the dataset. The visible customer sample does not display password hashes, so the bcrypt claim is not corroborated by that sample. The employee section shows field names rather than employee records, and no admin panel or authenticated session is demonstrated. Dates shown in sample records do not establish when the alleged breach occurred. No company confirmation is included in the supplied material.