Fédération Française de Spéléologie Dataset Claim Covers 93,493 Members
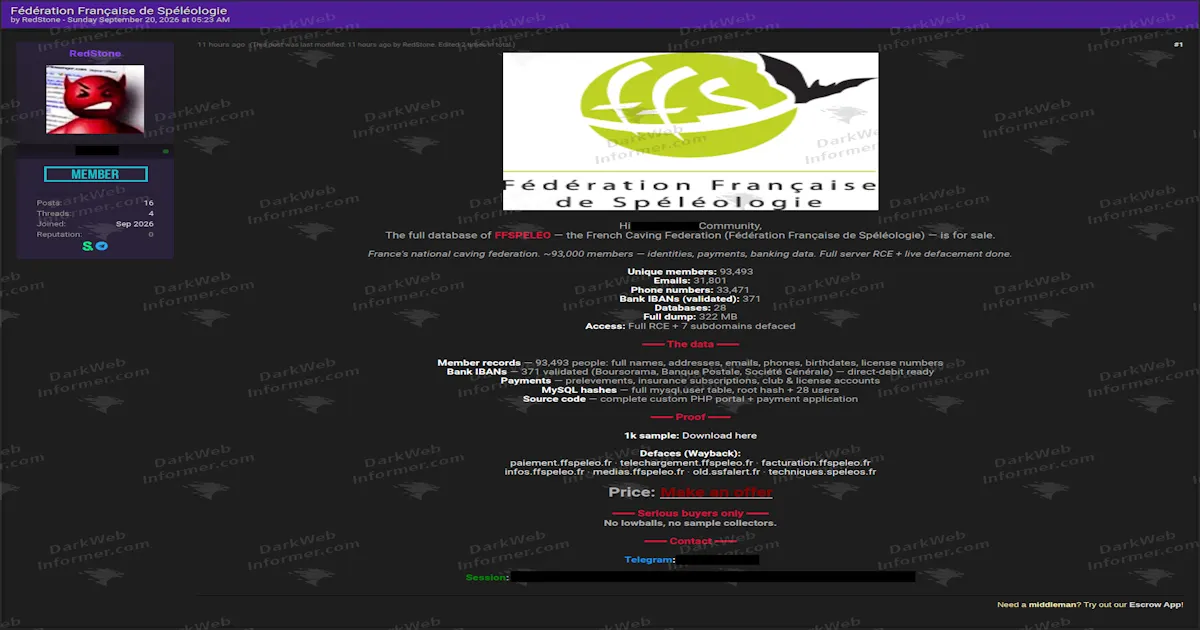
A forum actor posting as RedStone is offering what they claim is the full database of the Fédération Française de Spéléologie (FFS), France's national caving federation. The listing states that the material contains 93,493 unique member records, including 31,801 email addresses and 33,471 phone numbers. The actor also claims the dump includes 371 validated IBANs, payment and insurance-subscription data, club and license accounts, a full mysql.user table containing a root hash and 28 users, and the complete source code for a custom PHP portal and payment application. The post further claims full server RCE, compromise of 28 databases, a 322 MB dump, and defacement of seven subdomains. A 1,000-record sample is advertised. The claim is unverified.
▣Post details
!What the post claims
- 93,493 unique member records
- 31,801 email addresses
- 33,471 phone numbers
- Full names
- Home addresses
- Dates of birth
- License numbers
- 371 validated IBANs
- Banking information
- Payment and direct-debit data
- Insurance subscriptions
- Club accounts
- License accounts
- 28 databases
- 322 MB full dump
- Full mysql.user table
- Root password hash
- 28 MySQL users
- Complete custom PHP portal source code
- Payment-application source code
- Full server RCE claimed
- Seven subdomains allegedly defaced
- 1,000-record sample advertised
- Price listed as make an offer
◱Screenshot

☷Mapped techniques
The post does not explain how the initial compromise occurred. The techniques below are mapped only to capabilities and actions explicitly claimed in the listing.
- Collection T1213 Data from Information Repositories Claimed The actor claims access to 28 databases containing member, banking, payment, insurance and account records.
- Impact T1491.002 External Defacement Claimed The listing states that seven FFS-related subdomains were defaced and provides archived references as proof.
⚠Potential impact
If authentic, the combination of member identities, dates of birth, addresses, phone numbers, email addresses, license information and banking data could expose affected individuals to identity theft, targeted phishing, payment fraud and direct-debit abuse. The claimed IBAN data, payment records and insurance information increase the financial sensitivity of the incident. Exposure of the mysql.user table, root hash and application source code could also support follow-on attacks against federation systems if any credentials, secrets or vulnerabilities remain reusable. The claimed RCE and defacement activity would indicate that the incident extended beyond passive data theft if verified.
iStatus Unverified
The forum listing provides specific member, email, phone, IBAN, database and file-size counts, along with claims of server-level access, source-code theft and multiple defacements. However, the post does not identify the initial intrusion method or independently demonstrate that the advertised archive is complete and current. Dark Web Informer has not independently verified the 93,493-member dataset, the 371 IBANs, the claimed RCE, the MySQL credential material, the source-code archive or the seven defacement claims.
Dark Web Informer // Threat Intelligence