 United States
Travel & Photography
User Account Data
One-Time Sale
Unverified
Explorest Dataset Offered for One-Time Sale After Claimed Breach of 263,900 Users
Overview
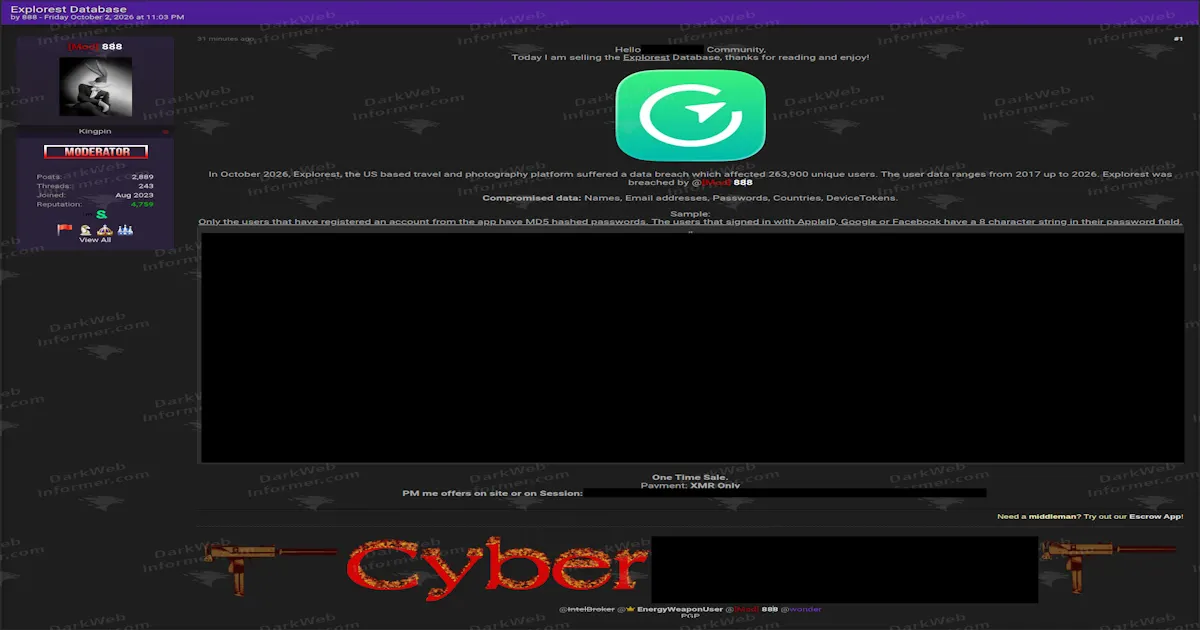
An actor using the handle "888" claims to be selling a dataset associated with Explorest, described in the listing as a U.S.-based travel and photography platform. The actor claims the material affects 263,900 unique users and spans data from 2017 through 2026.
The listing says the compromised data includes names, email addresses, passwords, countries and device tokens. It further claims that users who registered directly through the app have MD5-hashed passwords, while accounts created through Apple ID, Google or Facebook contain an eight-character string in the password field. The actor advertises the material as a one-time sale and requests payment in XMR. The dataset, its source, the claimed number of affected users and the authenticity of the sample have not been independently verified.
Post details
United StatesWhat the post claims
- 263,900 unique users affected
- Data ranges from 2017 through 2026
- Names included
- Email addresses included
- Password fields included
- Countries included
- Device tokens included
- MD5-hashed passwords claimed for direct app registrations
- Eight-character password-field strings claimed for social sign-in accounts
- Sample records displayed
- One-time sale advertised
- XMR-only payment requested
The visible sample contains structured account-profile fields including names, email addresses, password values, country, device-token data, profile identifiers, account metadata and social-login related fields. Personal information from the displayed sample is not transcribed in this report.
Screenshots

IOCs & contact identifiers
Identifiers directly visible in the listing. These support correlation and do not independently verify the dataset claim or identify the person operating the account.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | 888 | Screenshot 1 |
| Session ID | 054de8cc127c76f94eed19bbcc950fe9c9f6f9ef9f410f79e64989f480197a4476 | Screenshot 1 |
No Tox ID, malware hash, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material. Customer identifiers shown in the purported evidence are not included in this table. URLs to any data will always be blurred out, but are available for subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Inferred The listing presents structured application-user records containing account, profile and device-related fields. The supplied material does not reveal the acquisition method or establish unauthorized access to Explorest systems.
Potential impact
If authentic, the claimed dataset could expose names, email addresses, password-related values, countries and device tokens associated with Explorest users. Weak or reusable password hashes could increase credential-related risk, while email, profile and device information could support targeted phishing, impersonation and account-focused social engineering.
Status Unverified
Dark Web Informer has not independently verified the dataset's authenticity, source, claimed 263,900-user scope, data range, password details or current availability. The supplied material shows the listing and sample records rather than the full dataset.