
AFTT and FRBTT Breach Claim Includes 66,852 Subscribers and Plaintext Admin Passwords
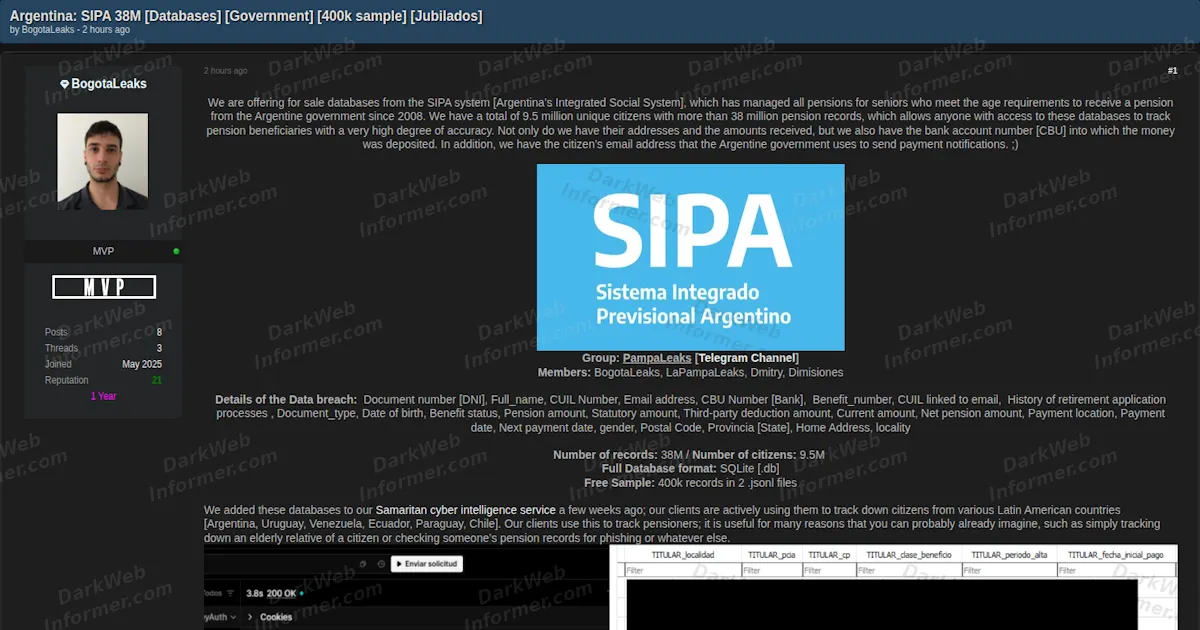
A forum actor posting as Venus1337 is selling what they claim is data belonging to AFTT, Aile Francophone de Tennis de Table, and FRBTT, Fédération Royale Belge de Tennis de Table. The actor claims the exposed material includes 66,852 subscriber records, 2,080 fine records, 17,441 user records and credentials for 87 club administrator accounts. According to the post, the compromise began with a remote code execution vulnerability in an insecure file-upload mechanism, after which the actor says they deployed a web shell, accessed SQL databases and found database credentials hardcoded in a file named secret.php. The actor further claims that multiple club-administrator passwords were stored in plaintext inside the CPHAdmin database and that approximately 1.69 GB of data was extracted. The claim is unverified.
▣Post details
!What the post claims
- 66,852 subscriber records
- 17,441 user records
- 2,080 fine records
- 87 club administrator accounts
- Plaintext club-admin passwords
- Approximately 1.69 GB of data
- Affiliation or membership numbers
- Names and first names
- Player class information
- Club names
- Club and division information
- Match categories and codes
- Sanction numbers and reasons
- Fine amounts
- User identifiers and usernames
- Email addresses
- Last-visit timestamps
- RCE through insecure file upload
- Web shell deployed after initial access
- Access to SQL databases
- Hardcoded database credentials in secret.php
◱Screenshots


☷Mapped techniques
The techniques below are based on methods explicitly described by the actor in the forum listing. Dark Web Informer has not independently verified the intrusion chain.
- Initial Access T1190 Exploit Public-Facing Application Claimed The actor claims a critical remote code execution vulnerability in an insecure file-upload mechanism was used to gain unauthorized access to the web server.
- Persistence T1505.003 Web Shell Claimed The actor states that a web shell was deployed after exploiting the file-upload weakness.
- Credential Access T1552.001 Credentials In Files Claimed The listing says SQL database credentials were hardcoded in a configuration file named secret.php.
- Collection T1213 Data from Information Repositories Claimed The actor claims access to SQL databases containing subscriber, user, fine and administrator records and says the databases were dumped in full.
⚠Potential impact
If authentic, the compromise could expose members, players and club personnel to phishing, impersonation and credential-based attacks. The most significant risk comes from the actor's claim that administrator passwords were stored in plaintext, which could allow those credentials to be reused against related systems if administrators used the same passwords elsewhere. Membership records, club affiliations, email addresses and account identifiers also provide useful context for targeted social engineering. A functioning web shell or unresolved file-upload vulnerability would further increase the risk of continued unauthorized access, database manipulation or follow-on compromise.
iStatus Unverified
The forum post provides a detailed intrusion narrative, claimed record counts and visible samples from files named adherents.jsonl, amendes.jsonl and users.jsonl. It also claims that database credentials were hardcoded and that club-administrator passwords were stored in plaintext. However, Dark Web Informer has not independently verified the vulnerability, the alleged web-shell access, the completeness of the 1.69 GB dump or the authenticity of the claimed administrator credentials.
Dark Web Informer // Threat Intelligence