
FLOCKER Ransomware Affiliate Program Returns With 90% Revenue Share and Cross-Platform Tooling
Overview
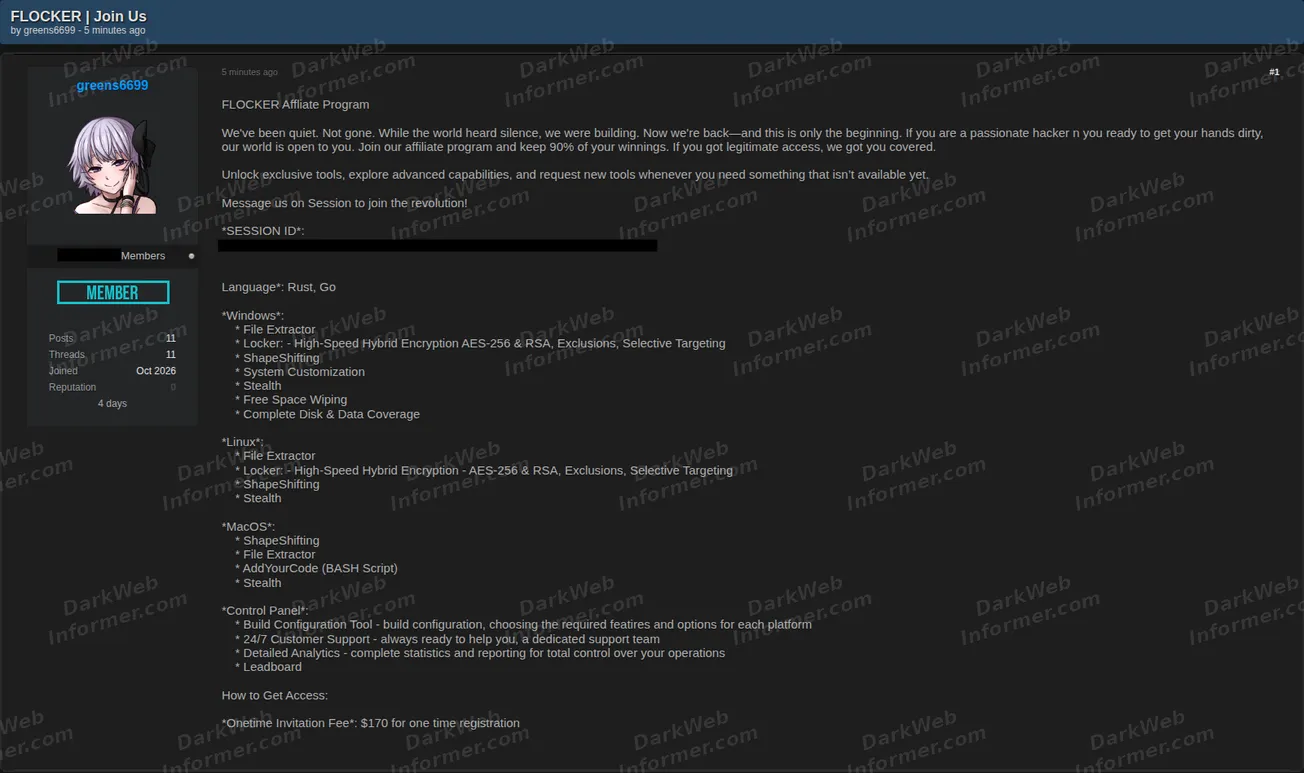
An actor using the handle "greens6699" is advertising the FLOCKER affiliate program and says the operation has returned after a period of inactivity. The post offers affiliates 90% of proceeds and states that operators will assist with obtaining legitimate access.
The advertisement describes tooling for Windows, Linux and macOS, along with a control panel for build configuration, analytics, customer support and affiliate rankings. Advertised capabilities include file extraction, encryption, stealth features, exclusions and selective targeting, customization, shape-shifting functionality and, for Windows, free-space wiping and complete disk/data coverage. The post lists Rust and Go as development languages and requires a $170 one-time invitation fee. The capabilities and operational claims have not been independently verified.
Post details
What the post advertises
- 90% affiliate revenue share
- Assistance obtaining legitimate access
- File extraction capability
- Windows locker using AES-256 and RSA
- Exclusions and selective targeting
- Shape-shifting capability
- System customization
- Stealth features
- Windows free-space wiping
- Windows complete disk and data coverage
- Linux locker capability
- macOS file extractor
- macOS custom code via Bash script
- Control-panel build configuration
- 24/7 customer support
- Detailed analytics
- Affiliate leaderboard
- $170 one-time invitation fee
The post presents FLOCKER as an active affiliate operation and describes a control panel intended to let affiliates configure builds and review operational statistics. No working samples, binaries or independent technical validation are shown in the supplied screenshot.
Screenshots
IOCs & contact identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently identify the person operating the account.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | greens6699 | Screenshot 1 |
| Session ID | 05e392b8fc91277ec543f3c0bc20320f5d649259138af35c0889b077a23014da74 | Screenshot 1 |
No Tox ID, Telegram handle, malware hash, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material. URLs to any data will always be blurred out, but are available for subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly advertised by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the capability has been independently validated.
- Impact T1486 Data Encrypted for Impact Claimed The advertisement explicitly describes locker functionality using encryption on Windows and Linux, consistent with data-encryption-for-impact behavior.
- Collection T1005 Data from Local System Inferred The advertised file-extraction capability suggests collection of local files before or alongside impact operations, although the screenshot does not show the implementation.
Potential impact
If the advertised capabilities are genuine, affiliates could use the service to support data theft, file encryption, operational disruption and extortion across Windows, Linux and macOS environments. The combination of selective targeting, build customization and claimed access support could increase operational flexibility for participating affiliates.
Status Observed
The supplied screenshot directly documents the FLOCKER recruitment advertisement and its stated features. Dark Web Informer has not independently verified that the advertised malware capabilities, control panel, affiliate payouts, support services or access-procurement claims are functional or currently operational.