
Spectator Loader Advertised as FUD Resident Loader With Anti-Analysis and Evasion Features
Overview
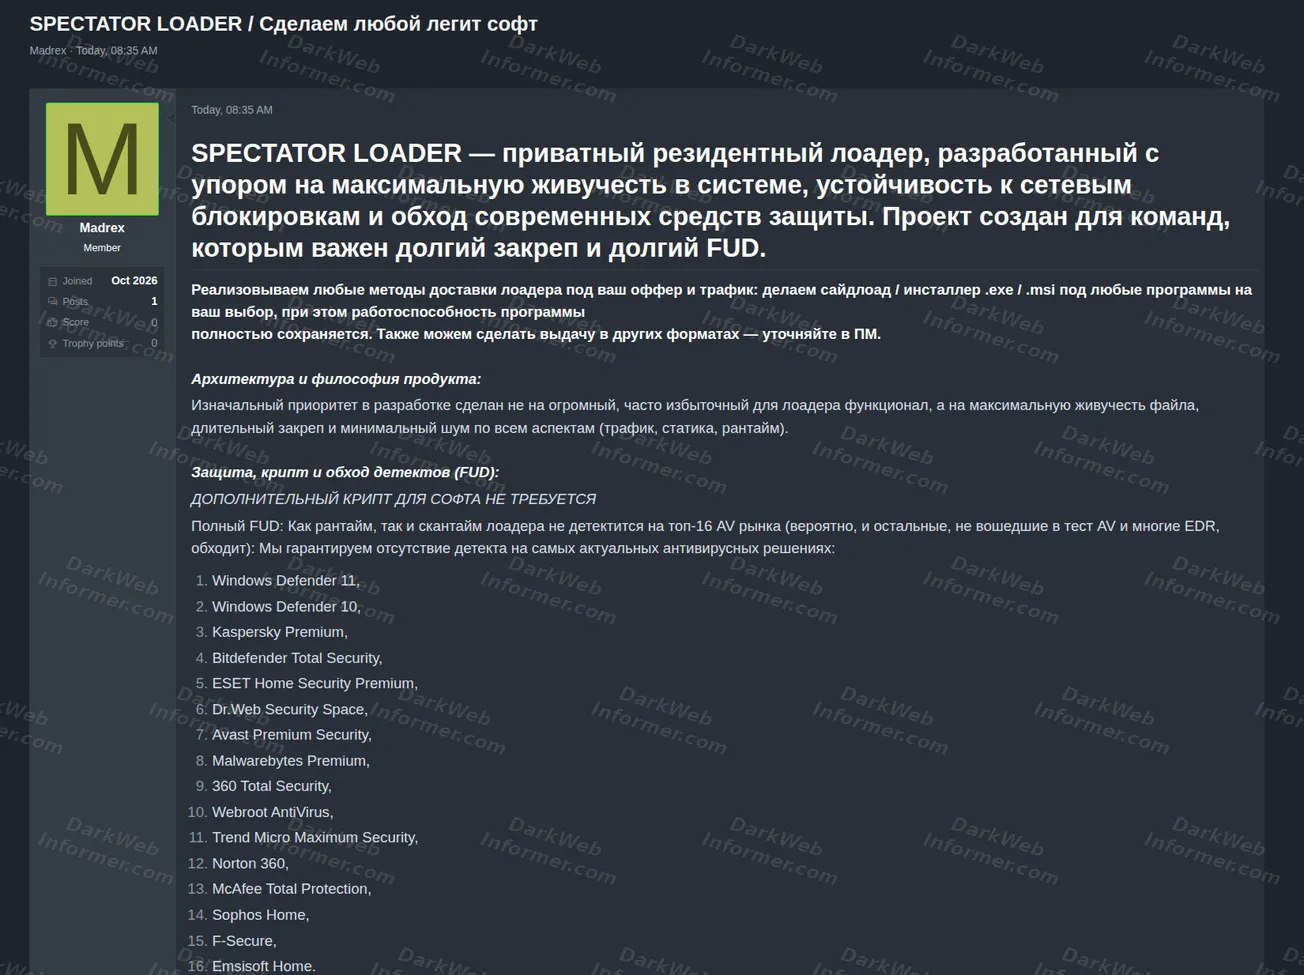
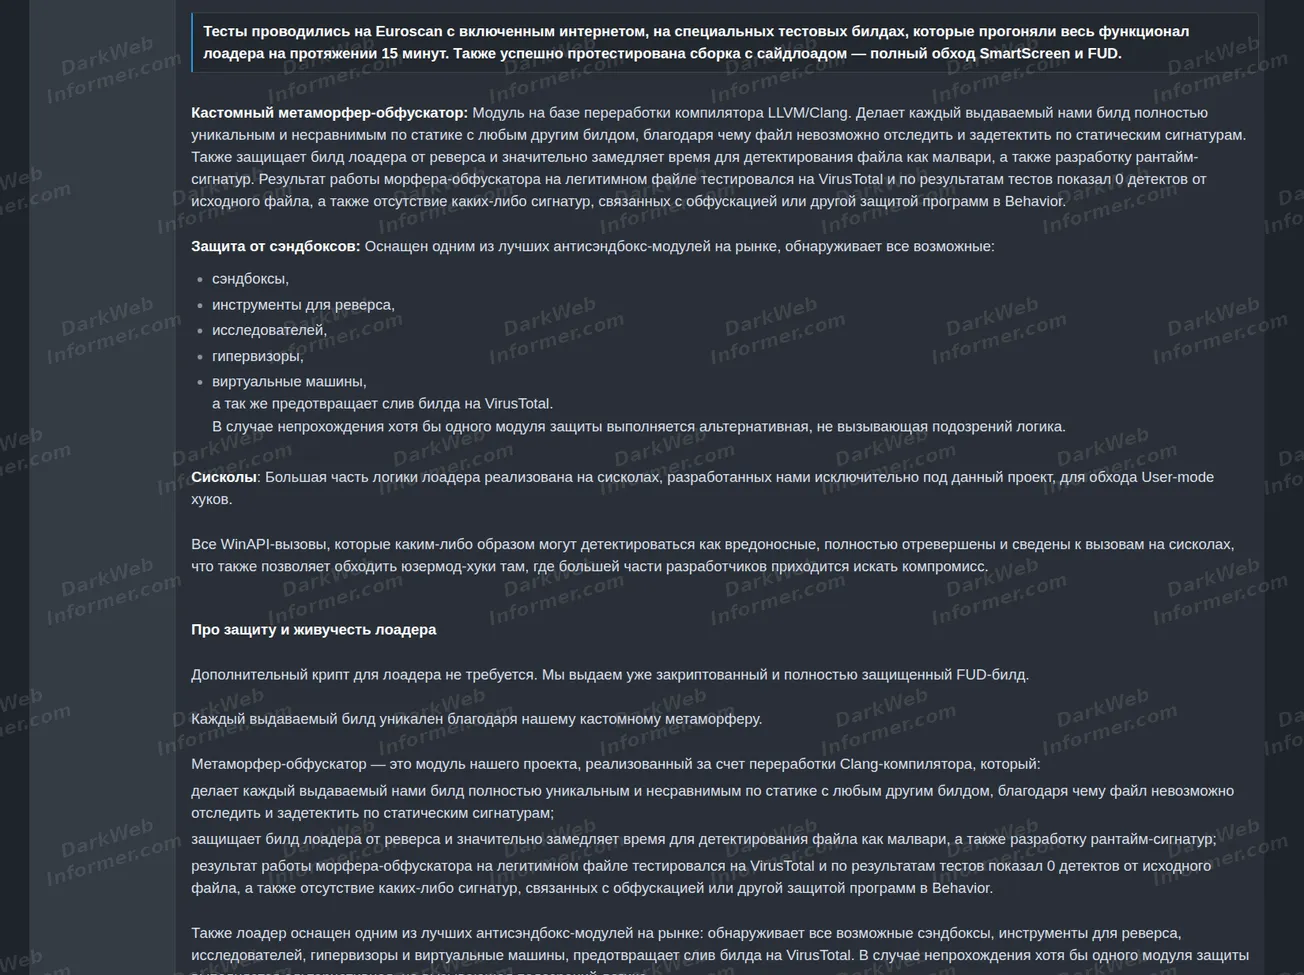
An actor using the handle "Madrex" is advertising a malware service called Spectator Loader. The Russian-language post describes it as a private resident loader built for long-term persistence, resistance to blocking and evasion of modern security products.
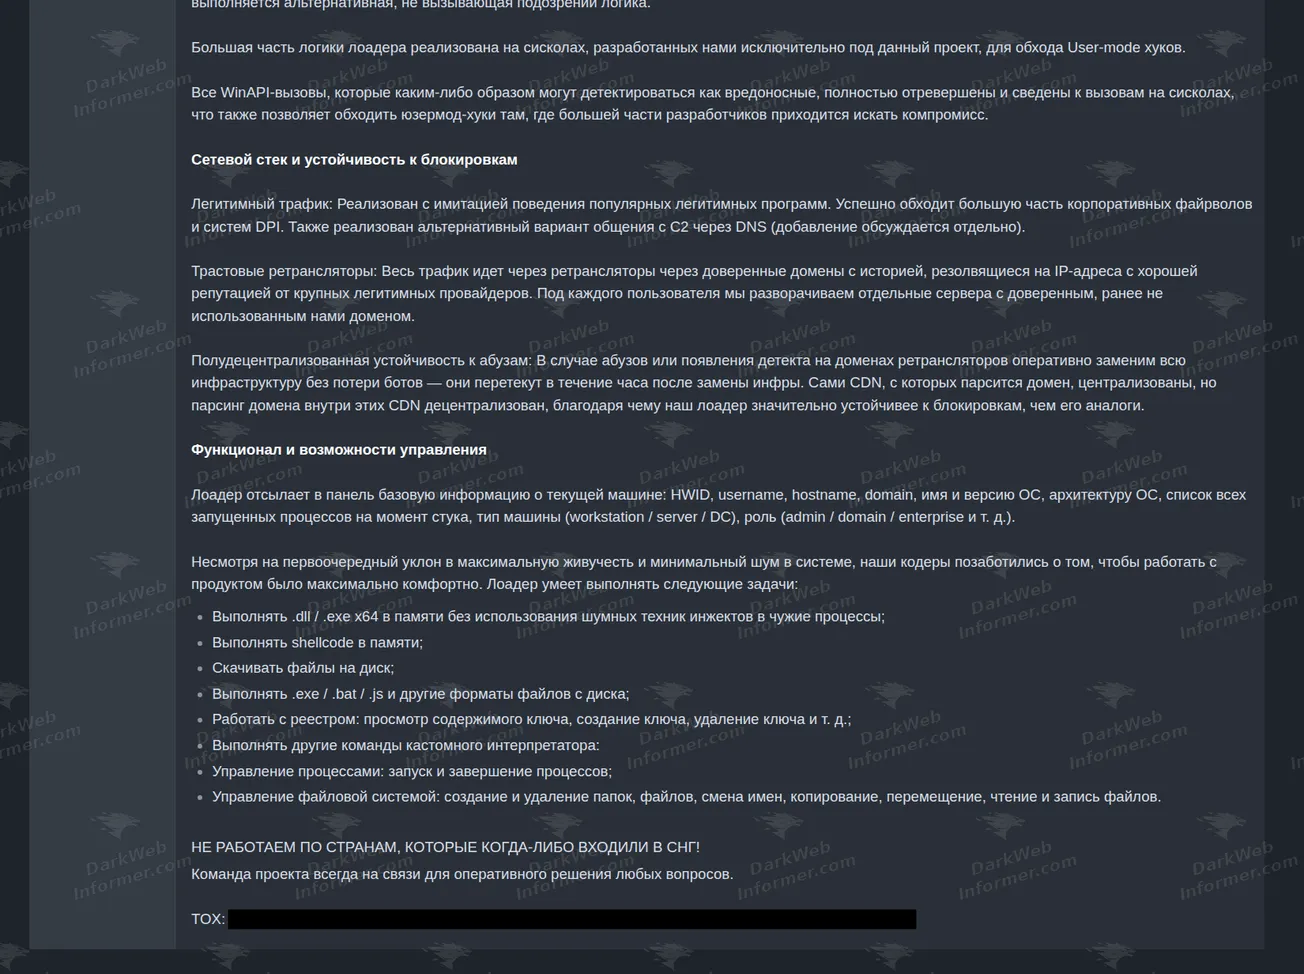
The advertisement claims the service can be delivered through sideloading or installer formats, uses custom obfuscation, anti-sandbox checks and low-level system-call techniques, and is designed to reduce static and behavioral detection. It also advertises remote-management capabilities such as system-information collection, in-memory payload execution, file transfer, process control, registry operations and filesystem management. These are actor claims from the advertisement and have not been independently validated.
Post details
What the post advertises
- Private resident loader
- Long-term persistence focus
- FUD / low-detection positioning
- Sideloading and installer delivery options
- Custom metamorphic obfuscation
- Anti-sandbox and anti-analysis checks
- Claims resistance to static signatures
- Claims reduced behavioral detection
- Low-level syscall-based execution claims
- Traffic imitation / trusted relay claims
- System-information collection
- In-memory payload execution
- File download capability
- Execution of multiple file/script formats
- Registry manipulation
- Process creation and termination
- Filesystem management
- Operator support advertised
The post also claims its protection stack can detect sandboxes, reverse-engineering tools, hypervisors and virtual machines, and that builds are altered to reduce similarity between samples. These statements are summarized as service claims and are not reproduced as implementation guidance.
Screenshots
IOCs & identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the advertised capabilities.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Madrex | Screenshots 1–3 |
| Service name | Spectator Loader | Screenshots 1–3 |
| Tox ID | 7EB9EF1A8CCCD4E02F87E0908BE745BE0F355D08B29CC1E74831AE80099A070BE4AD7E2E9B24 | Screenshot 3 |
No malware hash, Session ID, Telegram handle, attacker-controlled domain or attacker-controlled IP address is visible in the supplied screenshots.
Mapped techniques
Claimed identifies behavior explicitly advertised by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the capability has been independently validated.
- Defense Evasion T1027 Obfuscated Files or Information Claimed The advertisement explicitly promotes custom obfuscation and build-to-build variation intended to reduce static detection.
- Defense Evasion T1497 Virtualization/Sandbox Evasion Claimed The post claims the loader can detect sandboxes, virtual machines, hypervisors and reverse-engineering environments.
- Command and Control T1105 Ingress Tool Transfer Inferred The advertised management feature set includes downloading files to the compromised host.
Potential impact
If the advertised capabilities are genuine, Spectator Loader could provide operators with a stealth-focused foothold that supports payload delivery, in-memory execution, file transfer, process control, registry modification and filesystem access. Its anti-analysis and evasion claims could also increase the time required for defenders to identify and investigate malicious activity.
Status Unverified
Dark Web Informer has not independently verified the loader's detection-evasion claims, supported delivery methods, anti-sandbox behavior, network resilience or remote-management functionality. The supplied screenshots document the advertisement and visible contact information only.