 United States
IT Services
Source Code & Backups
Leak Claim
Unverified
Kensium Breach Claim Says 18 TB Exfiltrated, With 170 GB of Source Code and Database Backups Released
Overview
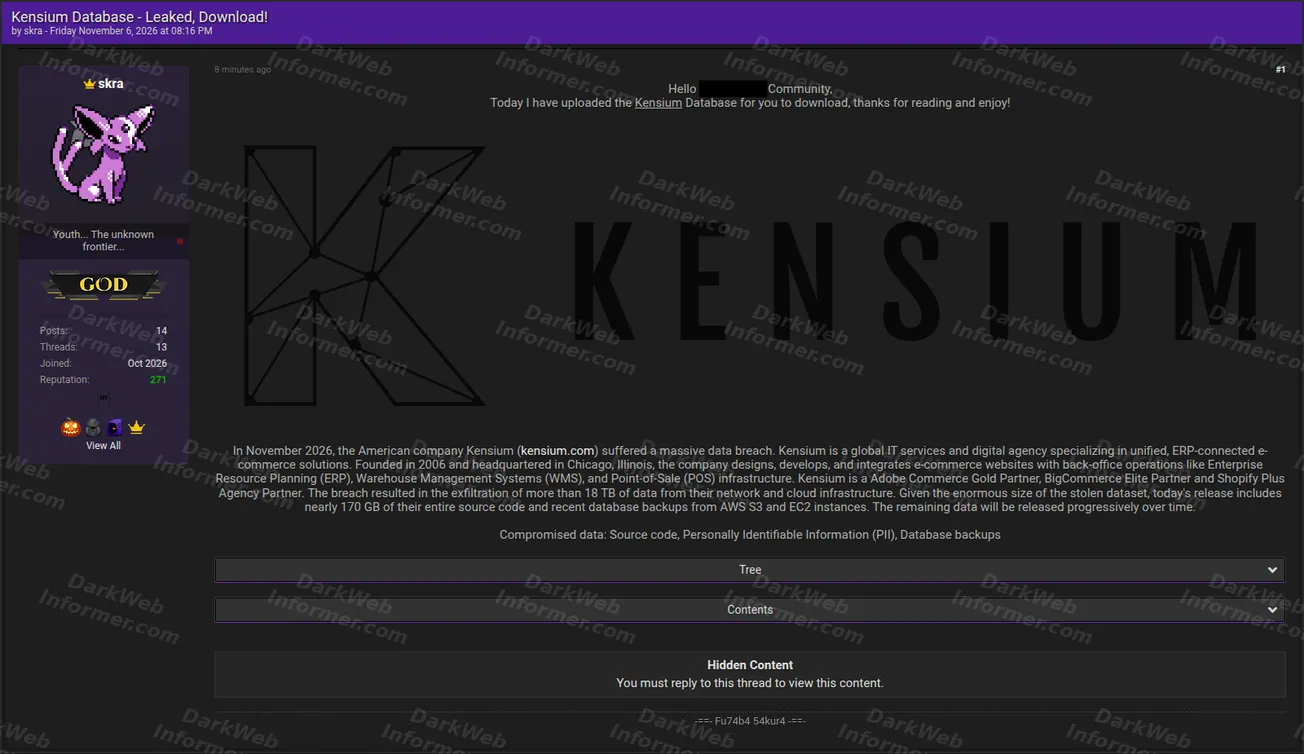
An actor using the handle "skra" claims to have uploaded a Kensium dataset. The post describes Kensium as a U.S.-based IT services and digital agency headquartered in Chicago, Illinois, specializing in ERP-connected e-commerce solutions.
The actor claims that more than 18 TB of data was exfiltrated from Kensium's network and cloud infrastructure. Because of the alleged size of the compromise, the current release is said to contain nearly 170 GB of source code and recent database backups from AWS S3 and EC2, with additional material intended to be released over time. The compromised-data categories are listed as source code, personally identifiable information and database backups. The breach, exfiltration volume, source-code archive, backup contents and current availability have not been independently verified.
Post details
United StatesWhat the post claims
- 18+ TB allegedly exfiltrated
- Nearly 170 GB released in the current batch
- Source code included
- Personally identifiable information included
- Recent database backups included
- AWS S3 data referenced
- EC2-hosted data referenced
- Additional releases planned over time
- Network and cloud infrastructure allegedly affected
- ERP, WMS and POS-connected e-commerce environment referenced
The source screenshot does not expose the hidden file tree or hidden archive contents, so the exact files, repositories, databases and personal-information categories cannot be confirmed from the supplied evidence alone.
Screenshots
IOCs & identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the breach claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | skra | Screenshot 1 |
| Named organization domain | kensium[.]com | Screenshot 1 |
The organization domain identifies the company named in the claim, not malicious infrastructure. No malware hash, Tox ID, Session ID, Telegram handle or attacker-controlled IP address is visible in the supplied screenshot.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1530 Data from Cloud Storage Inferred The listing explicitly references recent database backups from AWS S3 and data associated with EC2-hosted infrastructure.
- Collection T1213.003 Data from Information Repositories: Code Repositories Inferred The actor claims the release contains the company's source code, although the screenshot does not show the repository source or acquisition path.
Potential impact
If authentic, the claimed exposure could affect source code, customer or employee PII, database backups and cloud-hosted operational data. Source-code and backup exposure can increase risks of credential or secret leakage, application-security analysis, customer-data compromise, intellectual-property loss and follow-on attacks against integrated systems.
Status Unverified
Dark Web Informer has not independently verified the breach, claimed 18+ TB exfiltration volume, nearly 170 GB release, source-code contents, database backups, PII exposure or AWS data claims. The supplied screenshot documents the actor's listing only.