Corporate Access Buyer Seeks Privileged Network Entry Across U.S., Europe and LATAM
Overview
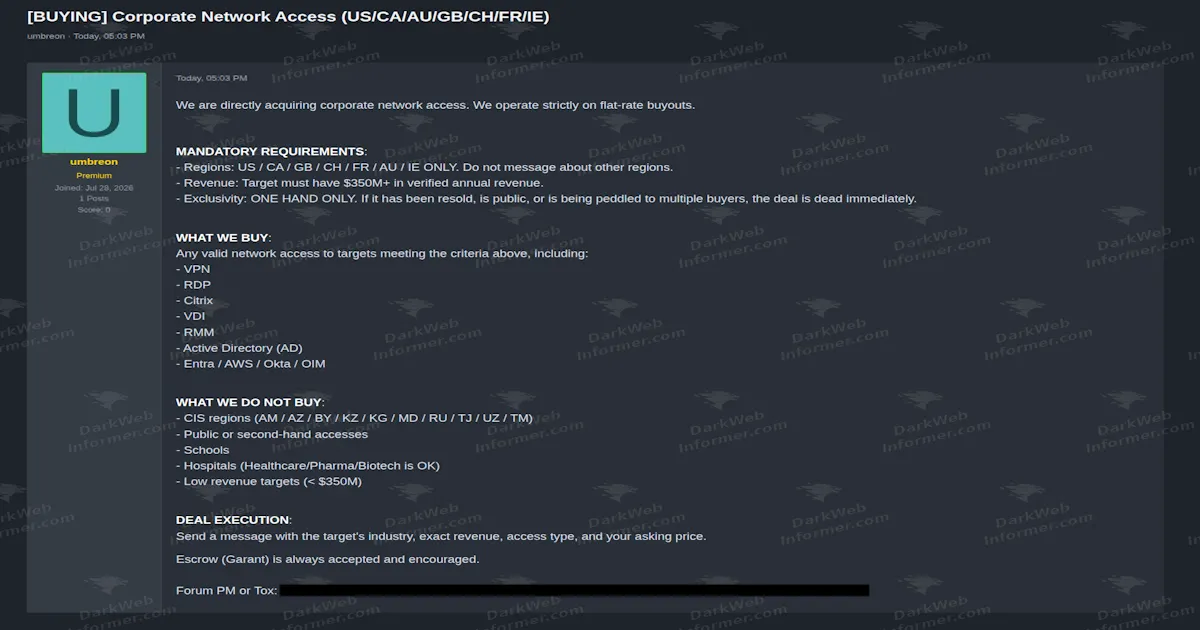
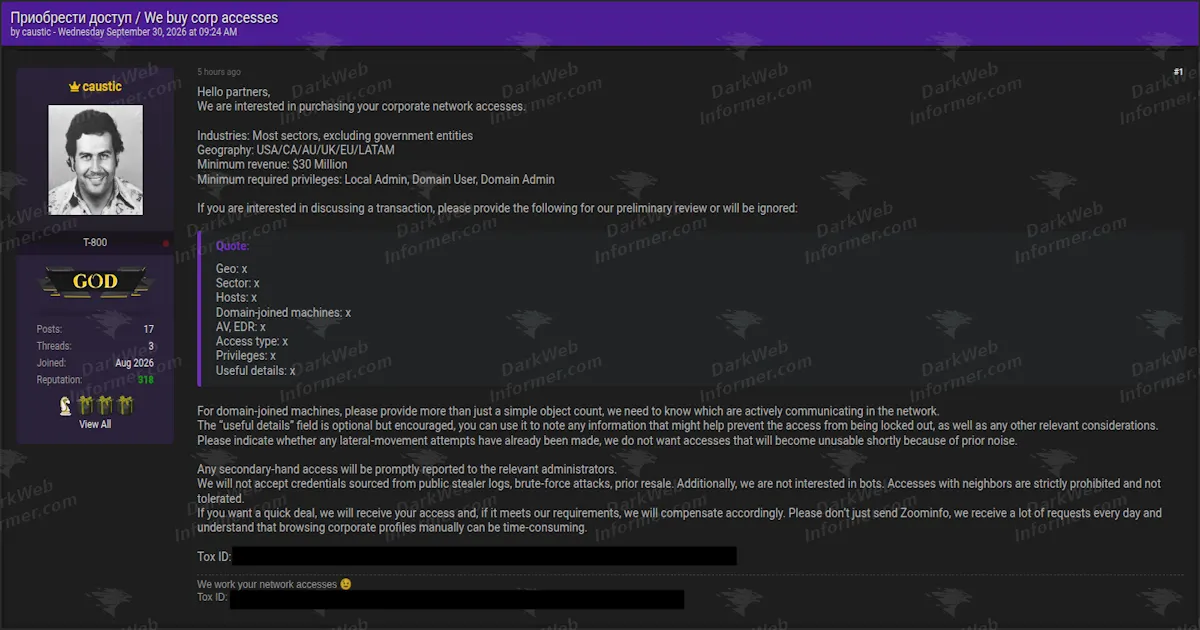
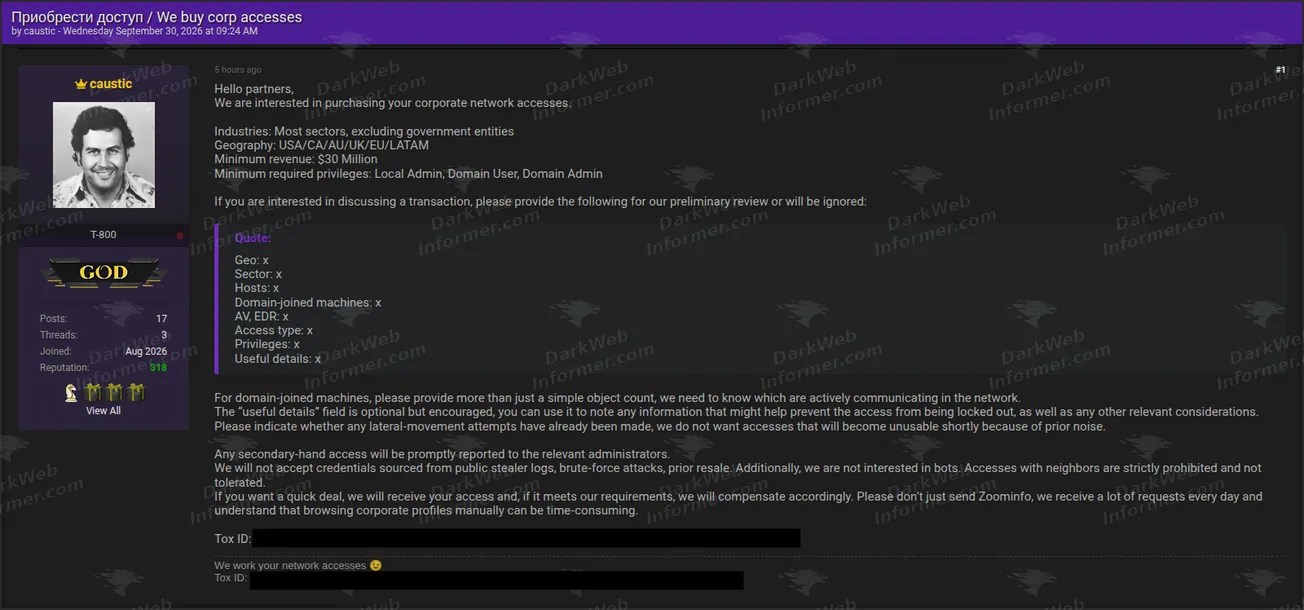
A poster using the handle "caustic" is advertising interest in purchasing access to corporate networks. The post says most industries are in scope except government entities and lists the United States, Canada, Australia, United Kingdom, European Union and Latin America as target geographies.
The buyer specifies a $30 million minimum revenue threshold and seeks access with privileges such as Local Administrator, Domain User or Domain Administrator. Sellers are asked to provide details about the environment, including geography, sector, host count, domain-joined systems, AV/EDR products, access type, privilege level and other useful context.
Post details
 USA
 Canada
 Australia
 UK
 EU
LATAM
What the post seeks
- Corporate network access
- Most industries accepted
- Government entities excluded
- Minimum company revenue of $30 million
- USA, Canada, Australia, UK, EU and LATAM
- Local Administrator access accepted
- Domain User access accepted
- Domain Administrator access accepted
- Geography and sector details requested
- Host count and domain-joined machine details requested
- AV and EDR information requested
- Access type and privilege level requested
- Lateral-movement history requested
- Public stealer-log credentials rejected
- Brute-forced or previously resold access rejected
- Bot access rejected
For domain-joined environments, the post asks sellers to provide more than a simple object count and instead identify systems that are actively communicating on the network. It also asks whether lateral-movement attempts have already been made and states that previously noisy access is undesirable because it may be blocked shortly afterward.
Screenshots
IOCs & contact identifiers
Identifiers directly visible in the supplied material. These support correlation but do not independently identify the person operating the account.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | caustic | Screenshot 1 |
| Tox ID | 11BA7BEFED534784A0507910CF5C179B8D00525FCD8EBA59F0DA62B7823EEE757CDC17A2FCD5 | Screenshot 1 |
No Session ID, malware hash, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material. URLs to any data will always be blurred out, but are available for subscribers on the threat feed or ransomware feed.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means downstream activity has been independently verified.
- Initial Access T1078 Valid Accounts Inferred The solicitation seeks usable corporate network access with local or domain-level privileges. The exact access vector is not specified, so this mapping reflects the requested use of established account-level access rather than a confirmed intrusion method.
Potential impact
If purchased access is valid, it could provide another threat actor with an established foothold inside a corporate environment. Depending on the privilege level and network exposure, that access could support credential abuse, lateral movement, data theft, extortion or ransomware deployment.
Status Observed
The supplied screenshot directly documents the access-buying solicitation and the listed requirements. Dark Web Informer has not independently verified the actor’s identity, purchasing capability, access to funds or whether any transactions were completed as a result of the post.