Conference-Space Company Breach Claim Says Access Remains Live With 6,027 Users and 115,948 Attachments
Overview
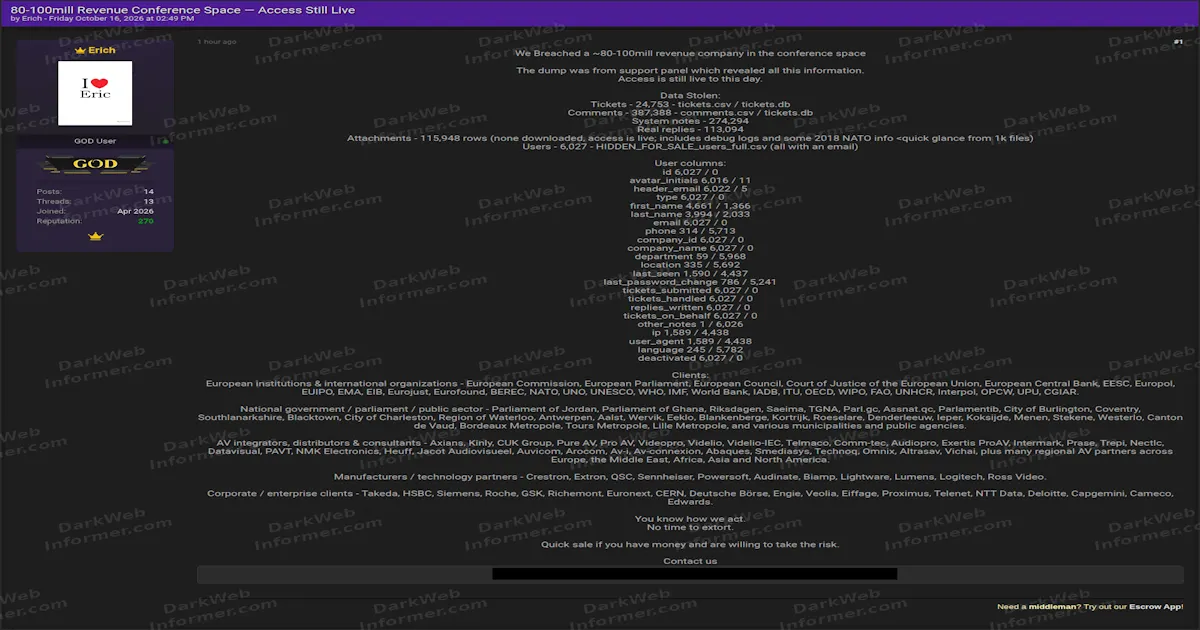
An actor using the handle "Erich" claims to have breached an unnamed conference-space company with approximately $80 million to $100 million in annual revenue. The actor says the compromise came through a support panel and claims that access remains active.
The post lists 24,753 tickets, 387,388 comments, 274,294 system notes, 113,094 real replies, 115,948 attachment rows and 6,027 users. The actor also claims the attachments include debug logs and some 2018 NATO-related material observed during a quick review. The breach, continued access, dataset contents and client associations have not been independently verified.
Post details
What the post claims
- 24,753 support tickets
- 387,388 comments
- 274,294 system notes
- 113,094 real replies
- 115,948 attachment rows
- 6,027 users
- All 6,027 users claimed to have an email address
- User IDs included
- Avatar initials included
- Email-header data included
- First and last names included
- Phone numbers included
- Company IDs and company names included
- Department and location fields included
- Last-seen timestamps included
- IP addresses and user-agent fields included
- Ticket and reply-count fields included
- Language and deactivation fields included
The actor says no attachment files were downloaded, but claims access to them remains available. The post also says a quick review of roughly 1,000 files showed debug logs and some NATO-related information from 2018.
Screenshots
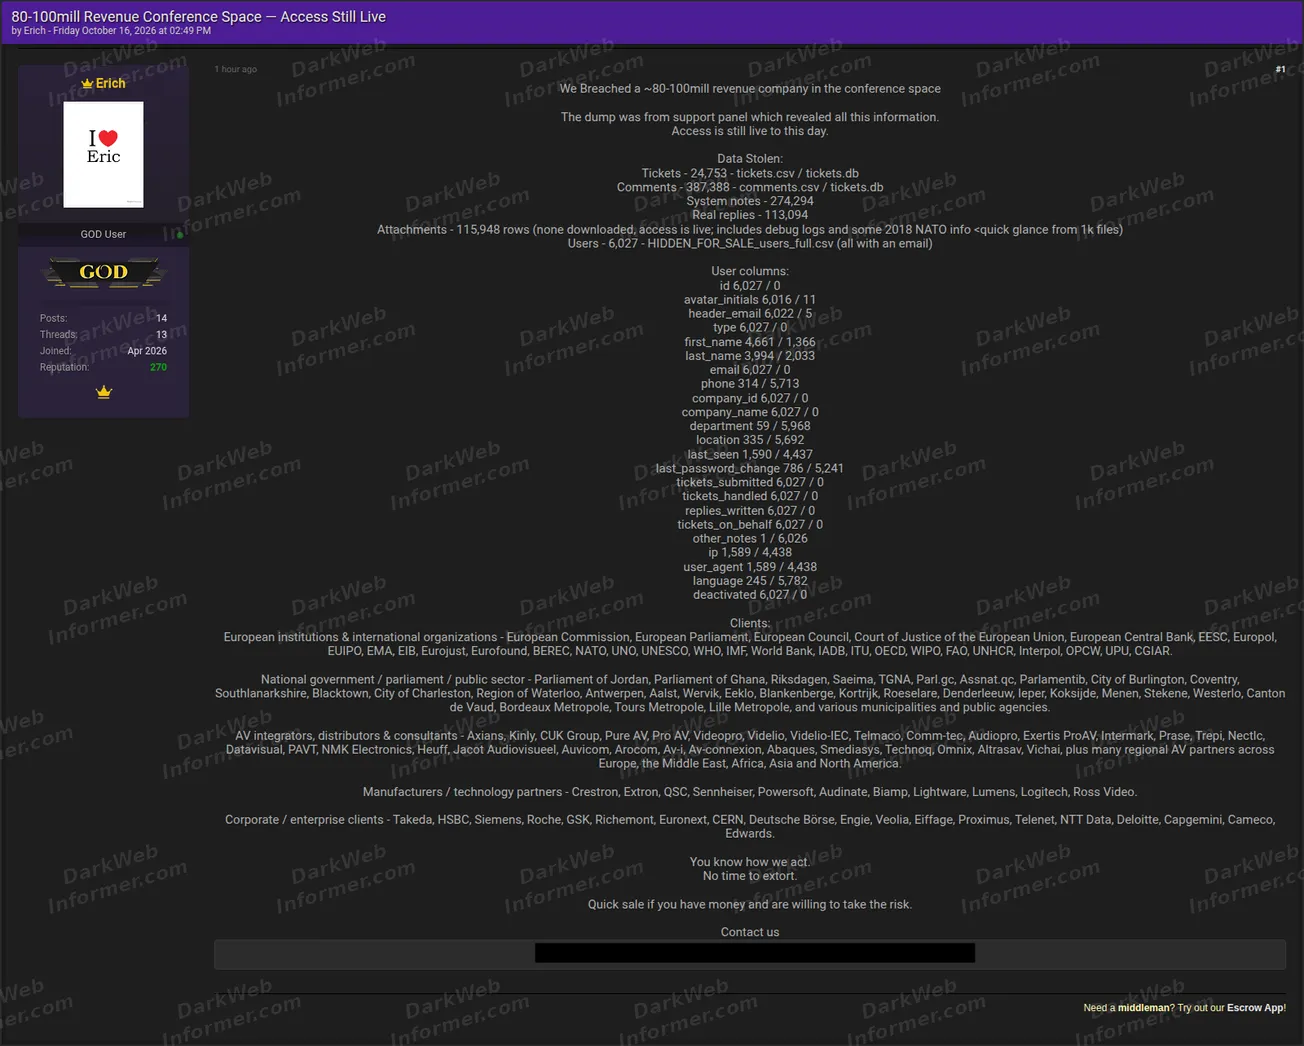
Client categories named
- European institutions and international organizations
- National governments, parliaments and public-sector bodies
- AV integrators, distributors and consultants
- Manufacturers and technology partners
- Corporate and enterprise clients
The actor names numerous public-sector, international, technology and enterprise organizations as clients of the breached company. The screenshot does not establish that those organizations were themselves directly compromised.
IOCs & identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the breach claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Erich | Screenshot 1 |
| Session ID | 050d21ed580450edf8a9deb238f8da1fc2a0da3595e45ff570c92248ebce31ac58 | Screenshot 1 |
No victim domain, malware hash, Tox ID, Telegram handle or attacker-controlled IP address is visible in the supplied screenshot. The target company is not named in the source material.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213 Data from Information Repositories Inferred The actor claims to have extracted structured support-platform data including tickets, comments, notes, users and attachments.
- Collection T1119 Automated Collection Inferred The volume and structured export-style counts described in the post are consistent with bulk or automated collection if the claim is accurate.
Potential impact
If authentic, the claimed exposure could reveal support communications, user identity and contact data, company relationships, IP addresses, user-agent information and potentially sensitive attachment contents. Continued access would also increase the risk of additional data collection or exposure beyond the material already described.
Status Unverified
Dark Web Informer has not independently verified the compromise, target identity, claimed live access, revenue estimate, dataset counts, attachment contents or client relationships described by the actor. The supplied screenshot documents the claim and listed statistics, not independent confirmation of the underlying breach.