Cast AI Data Leak Claim Includes AWS, GCP and GitLab Backups Across 20 GB Archive
Overview
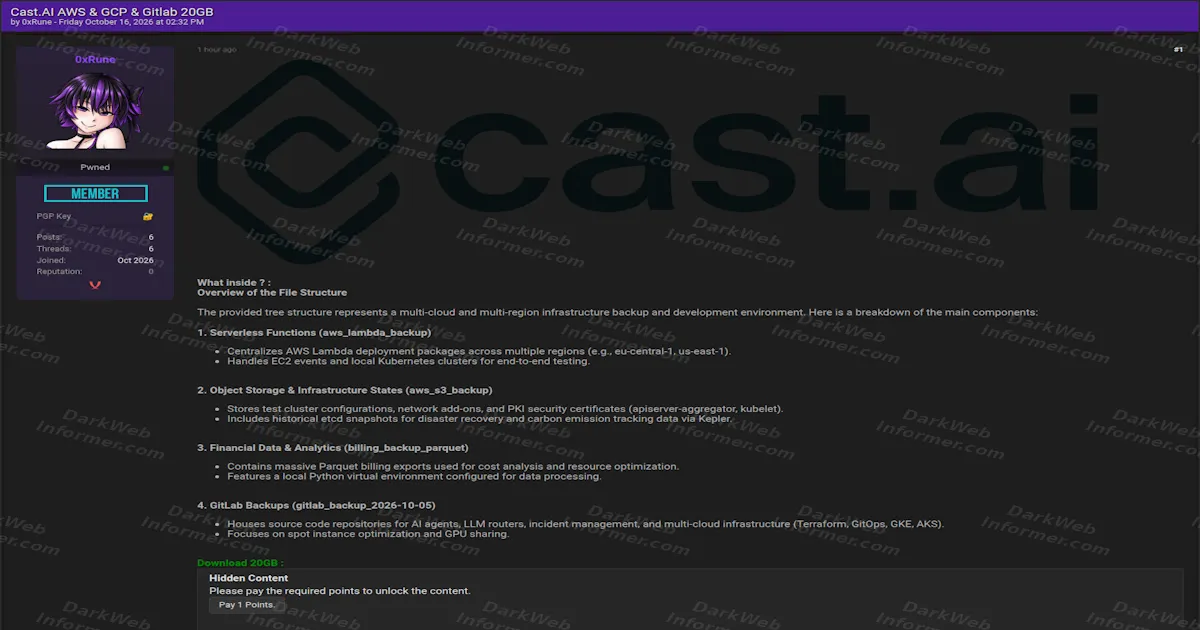
An actor using the handle "0xRune" claims to have uploaded approximately 20 GB of Cast AI data. The listing describes the material as a multi-cloud and multi-region infrastructure backup and development environment containing AWS, GCP and GitLab-related data.
The post specifically references AWS Lambda deployment packages, S3 backups, infrastructure-state data, billing exports and a GitLab backup dated October 5, 2026. It also says the GitLab material contains source code for AI agents, LLM routers, incident-management tooling and multi-cloud infrastructure including Terraform, GitOps, GKE and AKS-related content. The archive, its source, the stated 20 GB size and the claimed contents have not been independently verified.
Post details
What the post claims
- 20 GB archive advertised
- AWS Lambda backup material
- Deployment packages across multiple AWS regions
- EC2 event handling references
- Local Kubernetes test-cluster material
- AWS S3 backup content
- Infrastructure-state and test-cluster configurations
- Network add-on configuration
- PKI security certificate material
- Historical etcd snapshots
- Billing exports in Parquet format
- GitLab backup dated October 5, 2026
- Source code for AI agents
- LLM router code
- Incident-management tooling
- Terraform and GitOps content
- GKE and AKS-related infrastructure code
- Spot-instance and GPU-sharing optimization code
The listing describes a mixed infrastructure and development-data collection rather than a single database. No underlying files, credentials, secrets or source-code contents are visible in the supplied screenshot.
Screenshots

IOCs & identifiers
Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the data claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | 0xRune | Screenshot 1 |
| Named organization domain | cast[.]ai | Screenshot 1 |
The domain identifies the organization named in the claim, not malicious infrastructure. No malware hash, Tox ID, Session ID, Telegram handle or attacker-controlled IP address is visible in the supplied material.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.003 Data from Information Repositories: Code Repositories Inferred The listing explicitly references a GitLab backup containing source-code repositories and infrastructure code.
- Collection T1530 Data from Cloud Storage Inferred The post describes S3 backup content and cloud-hosted infrastructure data, consistent with collection from cloud storage if the claim is accurate.
Potential impact
If authentic, the claimed archive could expose source code, infrastructure configuration, deployment packages, PKI-related material, historical cluster state, billing data and multi-cloud operational details. Depending on the underlying files, that could create risks involving source-code disclosure, credential or secret exposure, infrastructure mapping, supply-chain abuse or follow-on compromise.
Status Unverified
Dark Web Informer has not independently verified the archive's authenticity, source, 20 GB size, backup dates, file structure or current availability. The supplied screenshot documents the listing and the actor's summary of the archive, not independent confirmation of the underlying files.