 Thailand
Media
Member & Infrastructure Data
Leak Claim
Unverified
Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure Dump
Overview
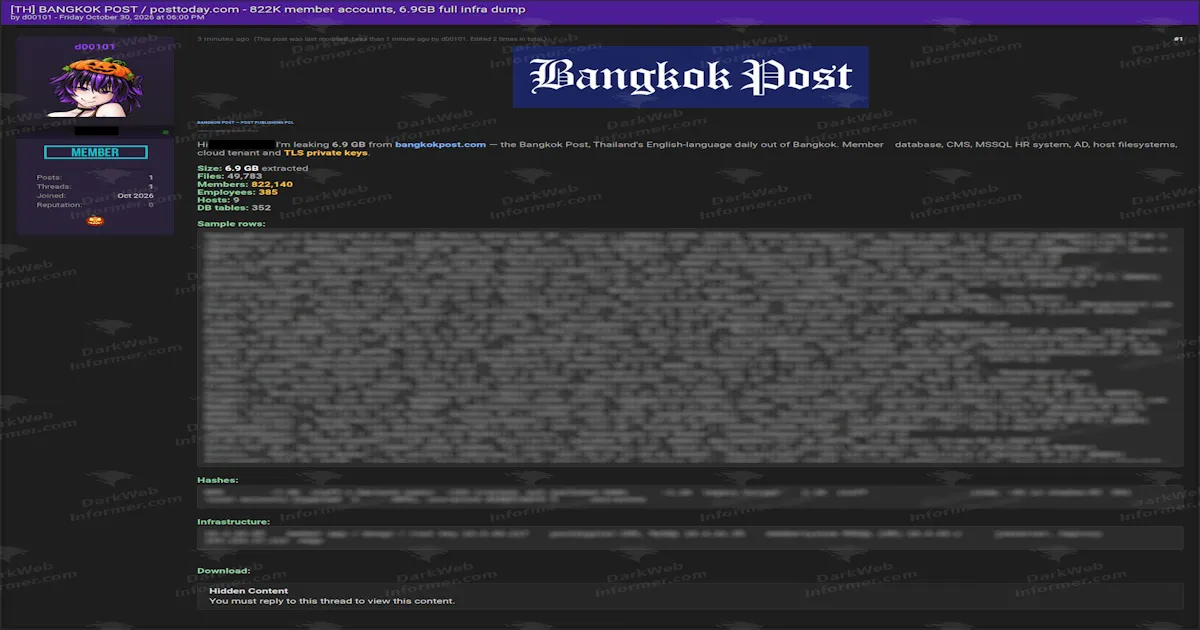
An actor using the handle "d00101" claims to have leaked approximately 6.9 GB of data associated with Bangkok Post, including member data and internal infrastructure material.
The listing advertises 49,783 files, 822,140 member records, 385 employee records, 9 hosts and 352 database tables. The actor says the dump includes member databases, CMS data, an MSSQL HR system, Active Directory-related material, host filesystems, cloud-tenant data and TLS private-key material. The breach, dataset contents, record counts and infrastructure claims have not been independently verified.
Post details
ThailandWhat the post claims
- 6.9 GB extracted
- 49,783 files
- 822,140 member records
- 385 employee records
- 9 internal hosts referenced
- 352 database tables
- Member database material included
- CMS data included
- MSSQL HR system data included
- Active Directory-related material included
- Host filesystem data included
- Cloud-tenant data included
- TLS private-key material claimed
- Password-hash material listed
- Sample member records displayed
- Internal infrastructure services listed
The actor also lists password-hash collections using MD5, SHA-1 and bcrypt and claims that a portion of the hashes were already cracked. The screenshot includes sample member emails, public IP addresses and internal infrastructure details; those values are not transcribed in this report.
Screenshots

IOCs & identifiers
Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the breach claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | d00101 | Screenshot 1 |
| Named organization domain | bangkokpost[.]com | Screenshot 1 |
The organization domain identifies the entity named in the claim, not malicious infrastructure. Internal RFC1918 addresses, private-key material, sample user emails and other sensitive values shown in the screenshot are intentionally not reproduced here.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Inferred The listing describes member, HR and application databases alongside hundreds of database tables.
- Collection T1005 Data from Local System Inferred The actor claims host filesystems and server-side material were included in the extracted data.
Potential impact
If authentic, the claimed exposure could affect member accounts, employee records, authentication material, internal systems and cryptographic assets. The combination of member data, password hashes, internal infrastructure information and claimed TLS key material could increase risks of account takeover, phishing, credential reuse, internal-system targeting and broader follow-on compromise.
Status Unverified
Dark Web Informer has not independently verified the breach, 6.9 GB extraction size, file counts, member or employee totals, password-hash claims, private-key claims, infrastructure access or current availability of the purported material. The supplied screenshot documents the actor's listing and visible evidence only.