 France
Healthcare Messaging
Professional & Contact Data
Download Listing
Unverified
APICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare Users
Overview
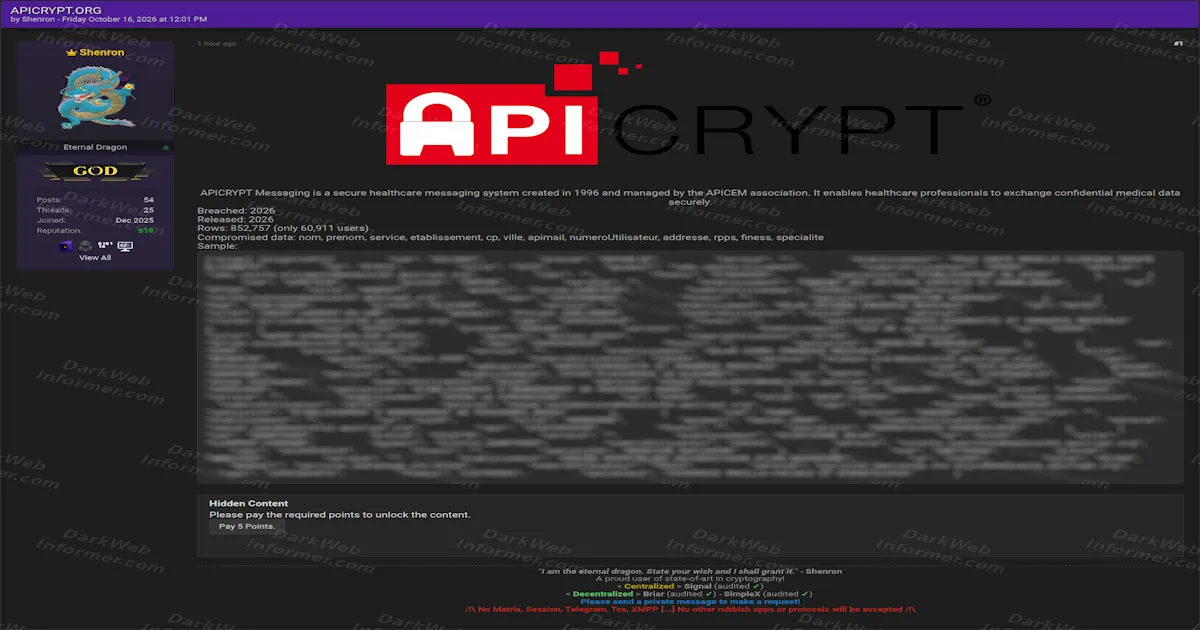
An actor using the handle "Shenron" claims to have released a dataset associated with APICRYPT Messaging, a secure healthcare messaging system created in 1996 and managed by the APICEM association.
The listing advertises 852,757 rows tied to 60,911 users. The visible field list includes surnames, given names, services, healthcare establishments, postal codes, cities, APICRYPT email addresses, user numbers, street addresses, RPPS identifiers, FINESS identifiers and specialties. The post marks the breach and release as occurring in 2026. The dataset, its source, the stated counts and current availability have not been independently verified.
Post details
FranceWhat the post claims
- 852,757 rows advertised
- 60,911 users advertised
- Breach dated to 2026
- Release dated to 2026
- Surname field listed
- Given-name field listed
- Service field listed
- Healthcare-establishment field listed
- Postal-code and city fields listed
- APICRYPT email-address field listed
- User-number field listed
- Street-address field listed
- RPPS identifier field listed
- FINESS identifier field listed
- Medical-specialty field listed
- Sample records displayed
- Hidden download requires 5 points
The visible sample contains healthcare-professional directory and contact information. Individual names, email addresses, RPPS numbers, FINESS identifiers and physical addresses shown in the sample are not transcribed in this report.
Screenshots
IOCs & identifiers
Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.
| Type | Identifier | Source |
|---|---|---|
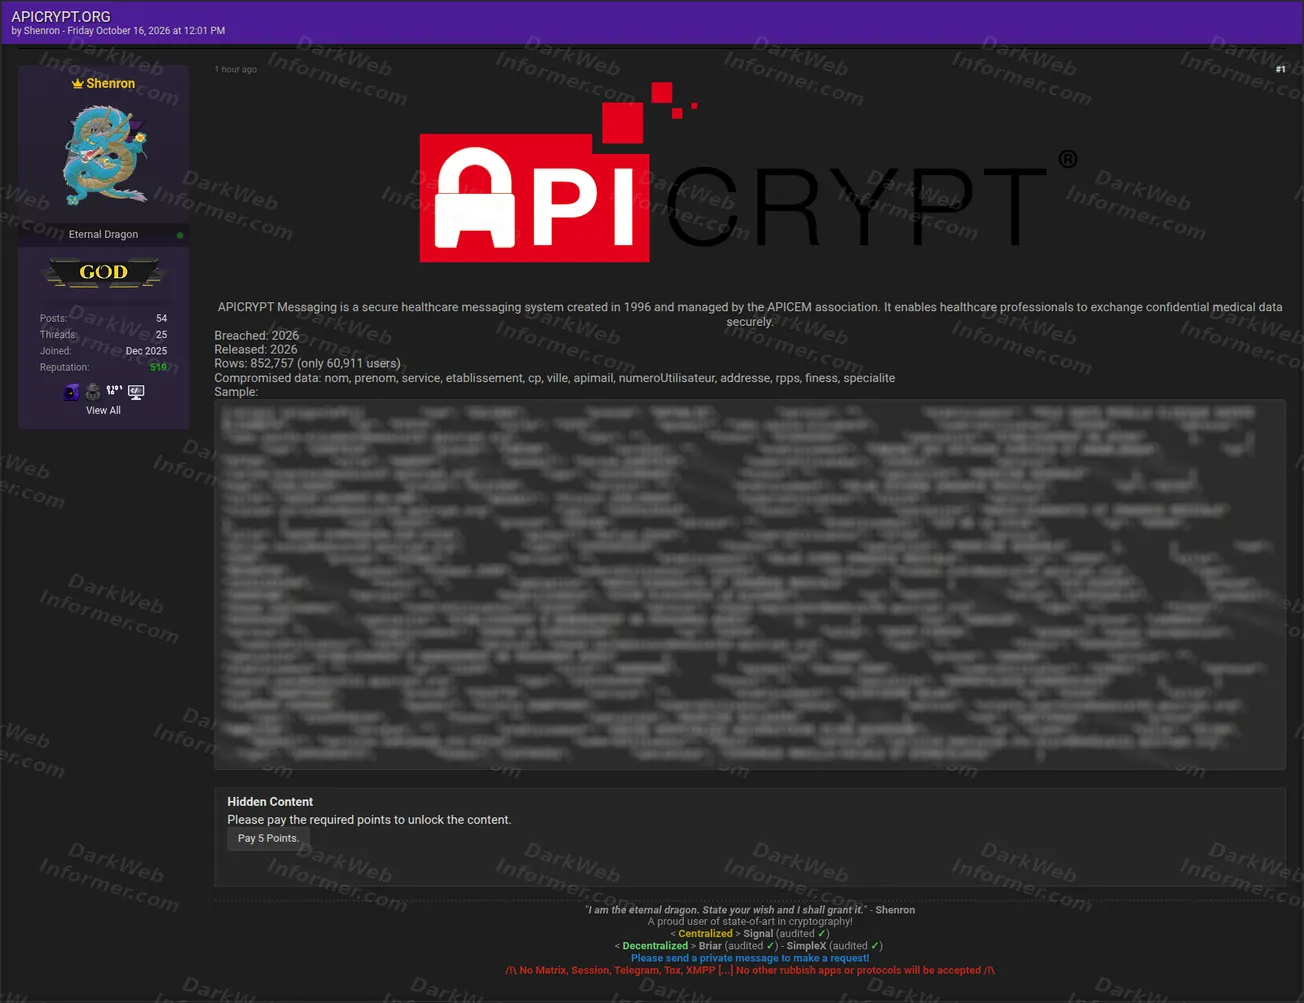
| Actor handle | Shenron | Screenshot 1 |
| Named organization domain | apicrypt[.]org | Screenshot 1 |
The domain identifies the organization named in the claim, not malicious infrastructure. The actor's footer explicitly states that Matrix, Session, Telegram, Tox and XMPP are not used. No malware hash, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material. Personal and professional identifiers shown in the sample are not included in this table.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Collection T1213.006 Data from Information Repositories: Databases Inferred The listing presents a structured dataset containing healthcare-professional identity, contact, organizational and professional-registration fields. The supplied material does not disclose how the data was obtained or independently establish unauthorized access to APICRYPT systems.
Potential impact
If authentic, the claimed dataset could expose healthcare-professional names, APICRYPT email addresses, physical addresses, RPPS identifiers, FINESS identifiers, specialties and workplace information. The combination could support targeted phishing, impersonation, credential-harvesting attempts or profiling of healthcare professionals and facilities.
Status Unverified
Dark Web Informer has not independently verified the dataset's authenticity, source, completeness, 852,757-row count, 60,911-user count, sample contents or current availability. The supplied screenshot documents the listing and visible sample records, not independent confirmation of the underlying dataset.